4399账号注册机.exe Ransomware Miner Analysis
Technical Analysis
| File Name | 4399账号注册机.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.215.174 |
| Database Version | 2025-04-30 16:00:22 UTC |
Ransom.Win32.Miner.cld
Malware family: Miner
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
d8e4072e31e5fa85702472715d3d9e59
|
|
| SHA1 |
f732e502a4bf4694746f5e71ee8847904ec828fc
|
|
| SHA256 |
7a01de7e472fa80b6a50eac2c220dedf506dd2e33ef6ec3dc92a4395f4a8bd2b
|
|
| SHA512 |
cb3674f078d9696f9e05cc9fb8e2ff9fcbda70cc25006c8c083691211c81e7f8cd98daede2683ca2cf926b1250aecca12654b7ccdb3ad4aefde10cb42e3a4d5e
|
|
| ImpHash |
13b9444f7fdc29e5f6651eca6ff9ee10
|
PE Analysis
Basic Information
▼| Icon |
Hash: 1fa61c049413b5ea14234b0662fb4006
Fuzzy: a1067b4196d17b78814e676232e220b2 dHash: f1d8a4b898b8a4c4 |
| Image Base | 0x00400000 |
| Entry Point | 0x0046da71 |
| Compilation Time | 2022-01-13 03:48:30 |
| Checksum | 0x00000000 (Actual: 0x000de45a) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 12 libraries |
| Exports | 0 functions |
| Resources | 56 Resources |
| Sections | 4 Sections |
Version Information
▼| FileVersion | 1.0.0.0 |
| FileDescription | 易语言程序 |
| ProductName | 4399注册机 |
| ProductVersion | 1.0.0.0 |
| LegalCopyright | 作者版权所有 请尊重并使用正版 |
| Comments | 本程序使用易语言编写(http://www.eyuyan.com) |
| Translation | 0x0804 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
573,214 bytes | 573,440 bytes | 6.57 (Compressed) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
5C7199E90B86DF9A2F8F6CC77D382E07 |
.rdata |
0x0008d000 |
184,166 bytes | 184,320 bytes | 6.60 (Compressed) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
1667D8EED3481A17B3F17B39356F4962 |
.data |
0x000ba000 |
199,624 bytes | 73,728 bytes | 5.09 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
14F305C629884C6AAECBF158540354B6 |
.rsrc |
0x000eb000 |
23,020 bytes | 24,576 bytes | 5.35 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
DB1E02DAD1927476E01DDF6544CC9221 |
Entropy Analysis Alert
2 section(s) with elevated entropy (≥6.5) - possible compression
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| TEXTINCLUDE | 3 | 370 bytes | |
| RT_CURSOR | 4 | 1,104 bytes | |
| RT_BITMAP | 15 | 6,404 bytes | |
| RT_ICON | 3 | 3,533 bytes | |
| RT_MENU | 2 | 656 bytes | |
| RT_DIALOG | 10 | 4,418 bytes | |
| RT_STRING | 11 | 2,268 bytes | |
| RT_GROUP_CURSOR | 3 | 74 bytes | |
| RT_GROUP_ICON | 3 | 60 bytes | |
| RT_VERSION | 1 | 580 bytes | |
| RT_MANIFEST | 1 | 461 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Ransom.Win32.Miner.cld Removal
Gridinsoft has the capability to identify and eliminate Ransom.Win32.Miner.cld without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
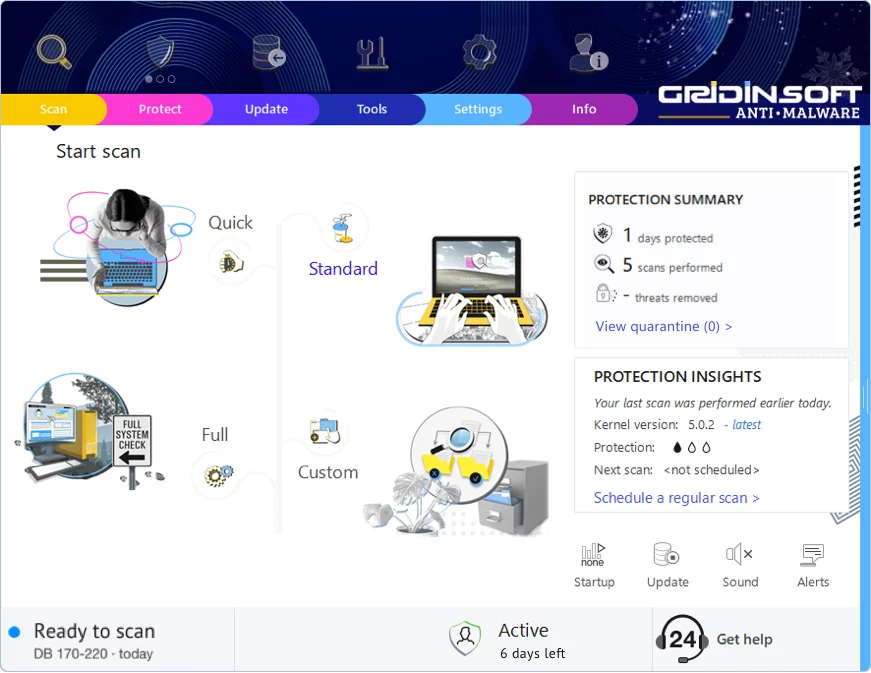
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!