MilwaukeeRivers.exe Stealer Gen Analysis
Technical Analysis
| File Name | MilwaukeeRivers.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.195.174 |
| Database Version | 2024-11-03 20:00:28 UTC |
Spy.Win32.Gen.tr
Malware family: Gen
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
e922a4d7d2c3c937231aa937b9a2ad25
|
|
| SHA1 |
b78ade0fbd78bff01d5c86079c9224d7b87f0770
|
|
| SHA256 |
bdc7b917477bb49af7a5b06e5d9ed20e08fed25944f297a6b36a50d03d8a5777
|
|
| SHA512 |
501a15eb4c5c64f2df9f454c11951907f33a834885113e14491a6823d8e3373c09523a3eedb52952aada8071dbeec88338dbdeb02a2c4d7a8e0af48eb1dbe5f6
|
|
| ImpHash |
be41bf7b8cc010b614bd36bbca606973
|
PE Analysis
Basic Information
▼| Icon |
Hash: beb7f2c0a209da13bb65188b9f61f121
Fuzzy: 225522008257bf535a74b24bd0af80a4 dHash: fef0e6e6daa69680 |
| Image Base | 0x00400000 |
| Entry Point | 0x00403883 |
| Compilation Time | 2012-02-24 19:19:54 |
| Checksum | 0x000ee8c8 (Actual: 0x000ee8c8) |
| OS Version | 5.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Digital Signature | The expected hash does not match the digest in SpcInfo |
| Imports |
8 libraries
KERNEL32, USER32, GDI32, SHELL32, ADVAPI32, COMCTL32, ole32, VERSION |
| Exports | 0 functions |
| Resources | 7 Resources |
| Sections | 6 Sections |
Version Information
▼| LegalTrademarks | BlockchainServerRapid360X is a trademark of RapidServer360 EliteBlockchain Technologies Co |
| ProductName | BlockchainServerRapid360X |
| Translation | 0x0409 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
28,078 bytes | 28,160 bytes | 6.51 (Compressed) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
00499A6F70259150109C809D6AA0E6ED |
.rdata |
0x00008000 |
10,850 bytes | 11,264 bytes | 4.39 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
07990AAA54C3BC638BB87A87F3FB13E3 |
.data |
0x0000b000 |
425,660 bytes | 512 bytes | 1.43 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
014871D9A00F0E0C8C2A7CD25606C453 |
.ndata |
0x00073000 |
528,384 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_UNINITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
D41D8CD98F00B204E9800998ECF8427E |
.rsrc |
0x000f4000 |
3,510 bytes | 3,584 bytes | 5.28 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
89EE89FE7851F158D99C5BFBF671994B |
.reloc |
0x000f5000 |
3,890 bytes | 4,096 bytes | 5.24 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
28EB16C084F743398EAC7A551641079B |
Entropy Analysis Alert
1 section(s) with elevated entropy (≥6.5) - possible compression
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 1 | 1,128 bytes | |
| RT_DIALOG | 3 | 636 bytes | |
| RT_GROUP_ICON | 1 | 20 bytes | |
| RT_VERSION | 1 | 528 bytes | |
| RT_MANIFEST | 1 | 726 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
The expected hash does not match the digest in SpcInfo
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Spy.Win32.Gen.tr Removal
Gridinsoft has the capability to identify and eliminate Spy.Win32.Gen.tr without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
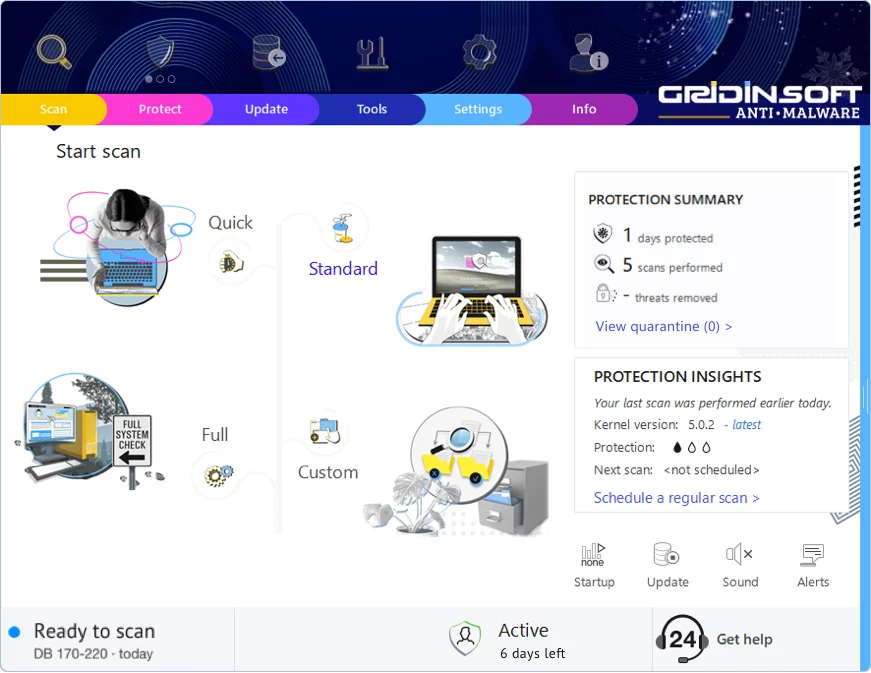
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!