Clicker banana.exe Stealer Keylogger Analysis
Technical Analysis
| File Name | Clicker banana.exe |
| File Type |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Scanner Version | 1.0.179.174 |
| Database Version | 2024-06-15 23:00:17 UTC |
Spy.Win64.Keylogger.oa!s1
Malware family: Keylogger
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
ab4e9d4671624ea0751f81bec0fd10e2
|
|
| SHA1 |
898368a3c2af2b1ae8c2896083eda14abdc63487
|
|
| SHA256 |
694d25ad6bb3db60612710b497e5f2ab5641d2b796a0625e758bbb2bb49b0091
|
|
| SHA512 |
a740999b6d8d66c39158652aee5887b1356077efa345895ff6eb3674ac584a1f8f074642dda2b8ac766537de8a0adb820b1ccf9d6e045a541f9572005df75076
|
|
| ImpHash |
2ac23c52e7647c5bbea38e98bb68c652
|
PE Analysis
Basic Information
▼| Icon |
Hash: 93afe220808e30c930df2bb029ee1098
Fuzzy: e555e06a276978c32ed8efbc4ad0084c dHash: 71f092b2b2b2f071 |
| Image Base | 0x140000000 |
| Entry Point | 0x14000be20 |
| Compilation Time | 2024-06-10 03:58:42 |
| Checksum | 0x01075436 (Actual: 0x01075436) |
| OS Version | 5.2 |
| PEiD Signatures |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Digital Signature | The PE file does not contain a certificate table. |
| Imports |
5 libraries
USER32, COMCTL32, KERNEL32, ADVAPI32, GDI32 |
| Exports | 0 functions |
| Resources | 31 Resources |
| Sections | 6 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
167,776 bytes | 167,936 bytes | 6.48 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
DE5B7DEEB13436557C4BA84AA3D5B3FB |
.rdata |
0x0002a000 |
75,024 bytes | 75,264 bytes | 5.76 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
3B210A5225FF13943BE54F8107178AAC |
.data |
0x0003d000 |
29,640 bytes | 3,584 bytes | 1.83 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
8013C58834A08435A779FF436FF10EB7 |
.pdata |
0x00045000 |
8,640 bytes | 8,704 bytes | 5.43 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D16E38966953C987EB484AC72E115D6C |
.rsrc |
0x00048000 |
175,992 bytes | 176,128 bytes | 3.51 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
C1E5EB18391B4052DC6B7950F30D7ED1 |
.reloc |
0x00073000 |
1,896 bytes | 2,048 bytes | 5.28 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
BE4464056C7D34453C1E26C7294816EE |
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 29 | 172,704 bytes | |
| RT_GROUP_ICON | 1 | 412 bytes | |
| RT_MANIFEST | 1 | 1,293 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
The PE file does not contain a certificate table.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Spy.Win64.Keylogger.oa!s1 Removal
Gridinsoft has the capability to identify and eliminate Spy.Win64.Keylogger.oa!s1 without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
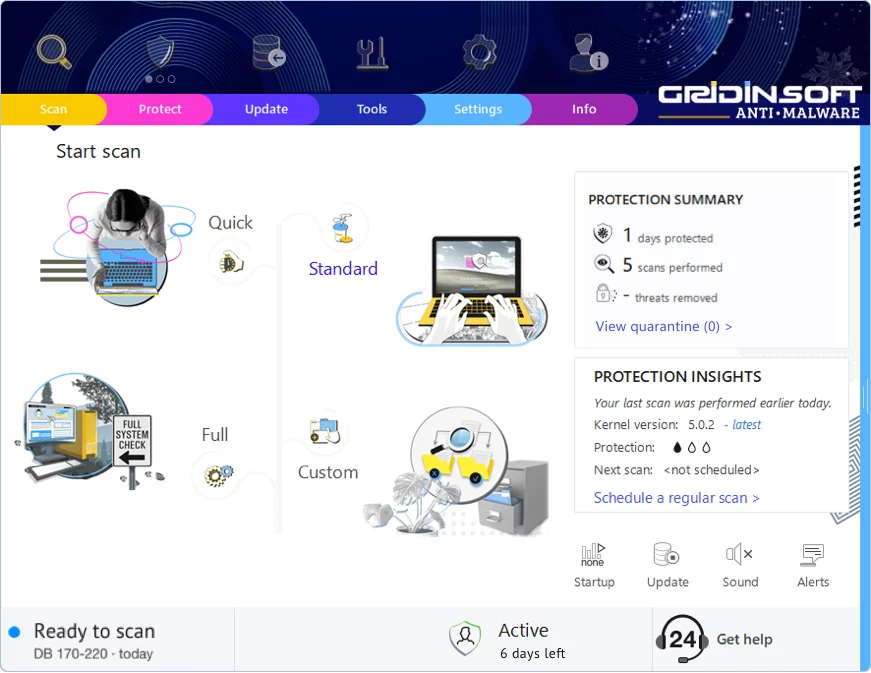
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!