Setuppopcon .exe Stealer Redline Analysis
Technical Analysis
| File Name | setuppopcon .exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.170.174 |
| Database Version | 2024-03-31 23:00:28 UTC |
Spy.Win32.Redline.lu!heur
Malware family: Redline
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
8fbdd0dc15e800dfdec30b5ee5201eca
|
|
| SHA1 |
4e8af1bbea3505603c1ae37d20f6bf7436cdd44d
|
|
| SHA256 |
0d5caf9c9e0da55980cda1dd5d9f3f95a8d1b12b0992030b995f49ce54b31f6c
|
|
| SHA512 |
c0b5146f425886b73301f0b2ca7fd6488cecca28b039e54ca6082b37e71dc814e0f82dec0dc74cae11cce833805a53a6b6690a5392a04a7d26b7d105841d41c3
|
|
| ImpHash |
646167cce332c1c252cdcb1839e0cf48
|
PE Analysis
Basic Information
▼| Icon |
Hash: 3e91cc67e146308239c15a39134ff14e
Fuzzy: 2e2cf0d16805fb9dfdfc9b2658485b99 dHash: f0f0f4d8c8c8d8f0 |
| Image Base | 0x00400000 |
| Entry Point | 0x00406d50 |
| Compilation Time | 2059-08-08 23:27:35 |
| Checksum | 0x019bbdaa (Actual: 0x019bbdaa) |
| OS Version | 10.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| PDB Path | wextract.pdb |
| Digital Signature | Chain verification from C=IE, [email protected], OU=Group Management, O=Know Your Customer Limited, CN=Claus Christensen (serial:-365698119444313454430775, sha1:504c13d2d98adecfc41cc61dc7dc9c4ce5f23091) failed: The X.509 certificate provided is self-signed - "Common Name: Claus Christensen, Organization: Know Your Customer Limited, Organizational Unit: Group Management, Email Address: [email protected], Country: IE" |
| Imports |
8 libraries
ADVAPI32, KERNEL32, GDI32, USER32, msvcrt, COMCTL32, Cabinet, VERSION |
| Exports | 0 functions |
| Resources | 56 Resources |
| Sections | 5 Sections |
Version Information
▼| CompanyName | Microsoft Corporation |
| FileDescription | Win32 Cabinet Self-Extractor |
| FileVersion | 11.00.22621.1 (WinBuild.160101.0800) |
| InternalName | Wextract |
| LegalCopyright | © Microsoft Corporation. All rights reserved. |
| OriginalFilename | WEXTRACT.EXE .MUI |
| ProductName | Internet Explorer |
| ProductVersion | 11.00.22621.1 |
| Translation | 0x0409 0x04b0 |
| CompanyName | Microsoft Corporation |
| FileDescription | Win32 Cabinet Self-Extractor |
| FileVersion | 11.00.22621.1554 (WinBuild.160101.0800) |
| InternalName | Wextract |
| LegalCopyright | © Microsoft Corporation. All rights reserved. |
| OriginalFilename | WEXTRACT.EXE .MUI |
| ProductName | Internet Explorer |
| ProductVersion | 11.00.22621.1554 |
| Translation | 0x0809 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
26,268 bytes | 26,624 bytes | 6.27 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
8EFCCDE25B9E492CDE40B5EF253CF7A7 |
.data |
0x00008000 |
6,816 bytes | 512 bytes | 4.97 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
7B9890A93C0516BB070E1170CFDE54D5 |
.idata |
0x0000a000 |
4,182 bytes | 4,608 bytes | 5.04 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
8FA33E292B5A9D9DCF9CF67D5C955B3D |
.rsrc |
0x0000c000 |
26,902,528 bytes | 26,901,504 bytes | 8.00 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
BA95CDEBC2F40CA51ADA3794EAF184E2 |
.reloc |
0x019b4000 |
2,184 bytes | 2,560 bytes | 6.27 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
0E9FAE0FC18F3412188D18FC97B6FC55 |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| AVI | 1 | 11,802 bytes | |
| RT_ICON | 13 | 85,490 bytes | |
| RT_DIALOG | 12 | 5,168 bytes | |
| RT_STRING | 12 | 12,414 bytes | |
| RT_RCDATA | 14 | 26,778,947 bytes | |
| RT_GROUP_ICON | 1 | 188 bytes | |
| RT_VERSION | 2 | 2,076 bytes | |
| RT_MANIFEST | 1 | 2,018 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
Chain verification from C=IE, [email protected], OU=Group Management, O=Know Your Customer Limited, CN=Claus Christensen (serial:-365698119444313454430775, sha1:504c13d2d98adecfc41cc61dc7dc9c4ce5f23091) failed: The X.509 certificate provided is self-signed - "Common Name: Claus Christensen, Organization: Know Your Customer Limited, Organizational Unit: Group Management, Email Address: [email protected], Country: IE"
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Spy.Win32.Redline.lu!heur Removal
Gridinsoft has the capability to identify and eliminate Spy.Win32.Redline.lu!heur without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
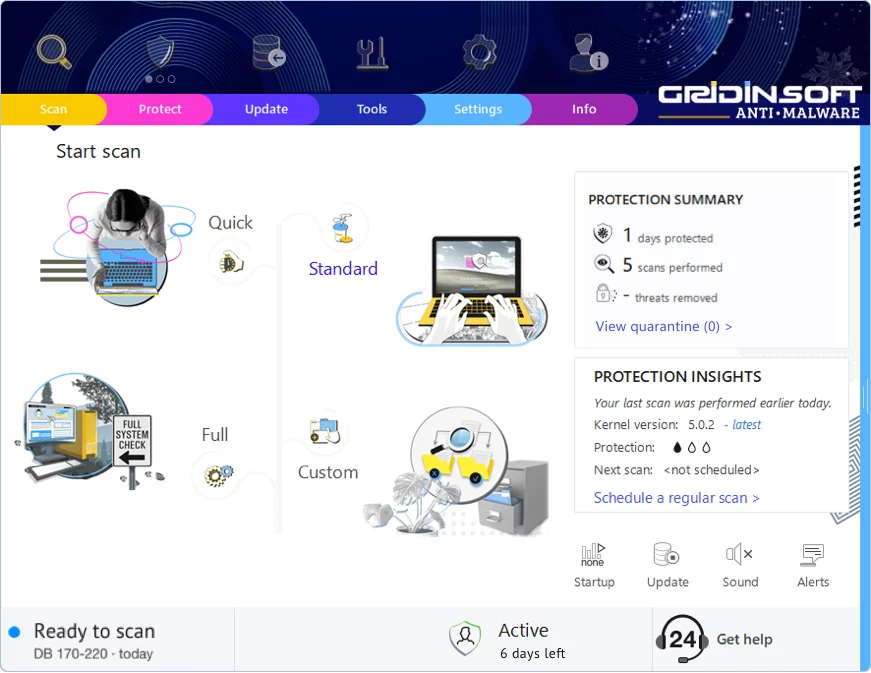
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!