Zipware-14-OCT-2018-V160.exe Stealer Redline Analysis
Technical Analysis
| File Name | Zipware-14-OCT-2018-V160.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.153.174 |
| Database Version | 2023-12-29 21:01:50 UTC |
Spy.Win32.Redline.lu!heur
Malware family: Redline
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
6ca55c007ce8fbac283ed4d03e2303b9
|
|
| SHA1 |
6c3246bf1a65416a9de4676bebc12854ba6741f7
|
|
| SHA256 |
0abd67edd302610c2f17419320c6a53dc1f441807e45e87b0c974d34ee6c3053
|
|
| SHA512 |
38873ab04a5b327b3d8a0850445911622f6c6ec3698c0729c6e8c8be9bd4a31c63e7f406401ef4e83e4c9d33699ecfd60ced43122a5c3622d3d7a4927125a6e4
|
|
| ImpHash |
bc70c4fa605f17c85050b7c7b6d42e44
|
PE Analysis
Basic Information
▼| Icon |
Hash: b4e35fab514a0ca7b15815d7b9e0ef39
Fuzzy: de7054b46a4aa933e23a31b431ec5c79 dHash: e862e2b26a6ab2ec |
| Image Base | 0x00400000 |
| Entry Point | 0x004067cc |
| Compilation Time | 2013-10-14 05:50:27 |
| Checksum | 0x0033ba0b (Actual: 0x0033ba0b) |
| OS Version | 6.3 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| PDB Path | wextract.pdb |
| Digital Signature | OK |
| Imports |
8 libraries
ADVAPI32, KERNEL32, GDI32, USER32, msvcrt, COMCTL32, Cabinet, VERSION |
| Exports | 0 functions |
| Resources | 36 Resources |
| Sections | 5 Sections |
Digital Signatures
▼| DigiCert SHA2 Assured ID Code Signing CA | Bazwise Technology (AU) |
| DigiCert Assured ID Root CA | DigiCert Inc (US) |
Version Information
▼| CompanyName | Microsoft Corporation |
| FileDescription | Win32 Cabinet Self-Extractor |
| FileVersion | 11.00.9600.16428 (winblue_gdr.131013-1700) |
| InternalName | Wextract |
| LegalCopyright | © Microsoft Corporation. All rights reserved. |
| OriginalFilename | WEXTRACT.EXE .MUI |
| ProductName | Internet Explorer |
| ProductVersion | 11.00.9600.16428 |
| Translation | 0x0409 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
26,060 bytes | 26,112 bytes | 6.38 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
E9BF1A1E456A9A811B1B86E6602E3636 |
.data |
0x00008000 |
6,796 bytes | 1,024 bytes | 3.18 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
317F8A934EE443EEE01C2A315BDE9CA1 |
.idata |
0x0000a000 |
4,216 bytes | 4,608 bytes | 5.05 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D8675BA112EF922C6057A02546757A1A |
.rsrc |
0x0000c000 |
3,336,015 bytes | 3,336,192 bytes | 8.00 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
5BF9B1BEA95FD8181F0D8E12E7689F2B |
.reloc |
0x0033b000 |
5,038 bytes | 5,120 bytes | 3.72 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
83DE2F9B2C95BE6FEA06BCED7E8A058E |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| AVI | 1 | 11,802 bytes | |
| RT_ICON | 6 | 22,384 bytes | |
| RT_DIALOG | 6 | 2,584 bytes | |
| RT_STRING | 6 | 6,208 bytes | |
| RT_RCDATA | 14 | 3,288,145 bytes | |
| RT_GROUP_ICON | 1 | 90 bytes | |
| RT_VERSION | 1 | 1,052 bytes | |
| RT_MANIFEST | 1 | 1,511 bytes |
Certificate Chain Analysis
▼Certificate #1
| Subject |
Bazwise Technology Bazwise Technology AU |
| Issuer | DigiCert SHA2 Assured ID Code Signing CA |
| Serial Number | 21010573155995391973643144543916334425 |
Certificate #2
| Subject |
DigiCert SHA2 Assured ID Code Signing CA DigiCert Inc US |
| Issuer | DigiCert Assured ID Root CA |
| Serial Number | 5364131601516814570659357524942475272 |
Certificate Verification Status
OK
Spy.Win32.Redline.lu!heur Removal
Gridinsoft has the capability to identify and eliminate Spy.Win32.Redline.lu!heur without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
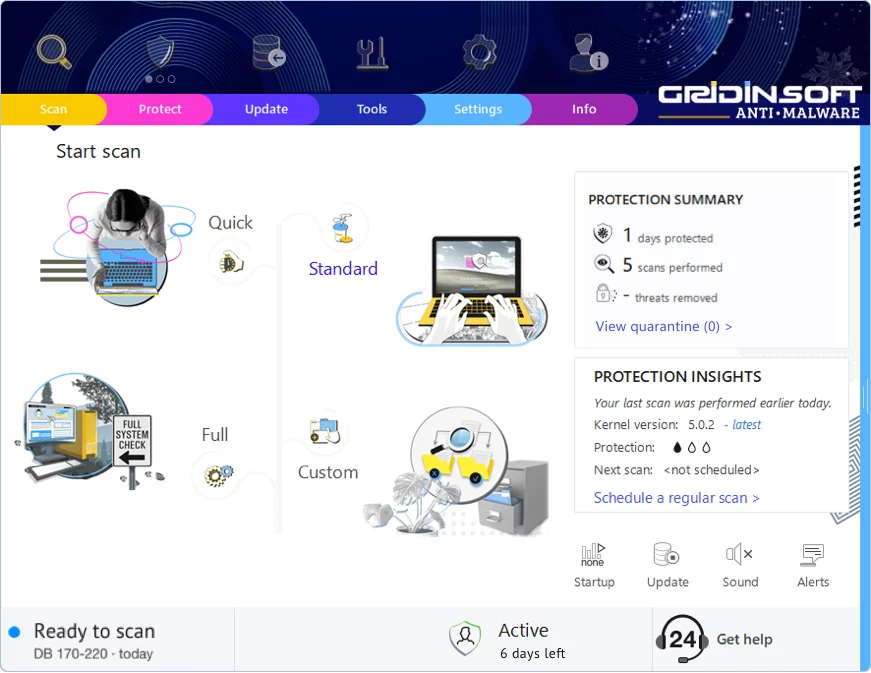
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!