Pr1.exe Backdoor Generic Analysis
Technical Analysis
| File Name | pr1.exe |
| File Type |
PE32 executable (GUI) Intel 80386 (stripped to external PDB), for MS Windows
|
| Scanner Version | 1.0.254.174 |
| Database Version | 2026-09-21 16:01:28 UTC |
Backdoor.Win32.Generic.oa!s1
Malware family: Generic
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
d87a65c6822d1cce2a15237edfcba355
|
|
| SHA1 |
5422fddddc2750b09c30ccd5a45ef4da056af8e9
|
|
| SHA256 |
c521ccd369d399c3c87ab1b6d3f9aa8c91f70ef4331fd1cea6413125258c6b00
|
|
| SHA512 |
7a43ff5a38da450069915cad7770982f3a0d2d437423a1cc19104ba5fb11dacae85678b8d1bd67b7241876e33ce3927a0bcf40efc8fff92e81815637c2aa63a5
|
|
| ImpHash |
818d3fa86f016cd06e99e723413c3e0d
|
PE Analysis
Basic Information
▼| Icon |
Hash: 6aa1e191a9aff15ea6d9b9a20b00609f
Fuzzy: fd10dbccdae6fa9597b1bfcce4c0e58c dHash: 818da080a0a080a0 |
| Image Base | 0x00400000 |
| Entry Point | 0x00401000 |
| Compilation Time | 2005-06-02 10:36:26 |
| Checksum | 0x00000000 (Actual: 0x001ffcd5) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386 (stripped to external PDB), for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 14 libraries |
| Exports | 531 functions |
| Resources | 6 Resources |
| Sections | 8 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
757,760 bytes | 755,200 bytes | 6.49 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
3C70391818008D47B60B741276CF8CAA |
.data |
0x000ba000 |
1,200,128 bytes | 1,180,160 bytes | 0.93 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
6F23435ABB6EB2D702B142C2BD0F45AA |
.tls |
0x001df000 |
4,096 bytes | 512 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
BF619EAC0CDF3F68D496EA9344137E8B |
.rdata |
0x001e0000 |
4,096 bytes | 512 bytes | 0.19 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_SHARED|IMAGE_SCN_MEM_READ
|
8D32A853890BAF863D4B5C8F1FB155F0 |
.idata |
0x001e1000 |
12,288 bytes | 12,288 bytes | 4.51 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
F7A11E40B32DC11EB795D6EB01B7D5B1 |
.edata |
0x001e4000 |
32,768 bytes | 30,208 bytes | 5.59 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
C507939605C361CD7DC7A185F28A5E7A |
.rsrc |
0x001ec000 |
7,328 bytes | 7,680 bytes | 4.88 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
DA37BAD809F8B3A44EA58773DB6ABAB1 |
.reloc |
0x001ee000 |
49,152 bytes | 47,104 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_SHARED|IMAGE_SCN_MEM_READ
|
B13FCB3223116F6EEC60BE9143CAE98B |
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 1 | 2,216 bytes | |
| RT_RCDATA | 4 | 4,635 bytes | |
| RT_GROUP_ICON | 1 | 20 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Backdoor.Win32.Generic.oa!s1 Removal
Gridinsoft has the capability to identify and eliminate Backdoor.Win32.Generic.oa!s1 without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
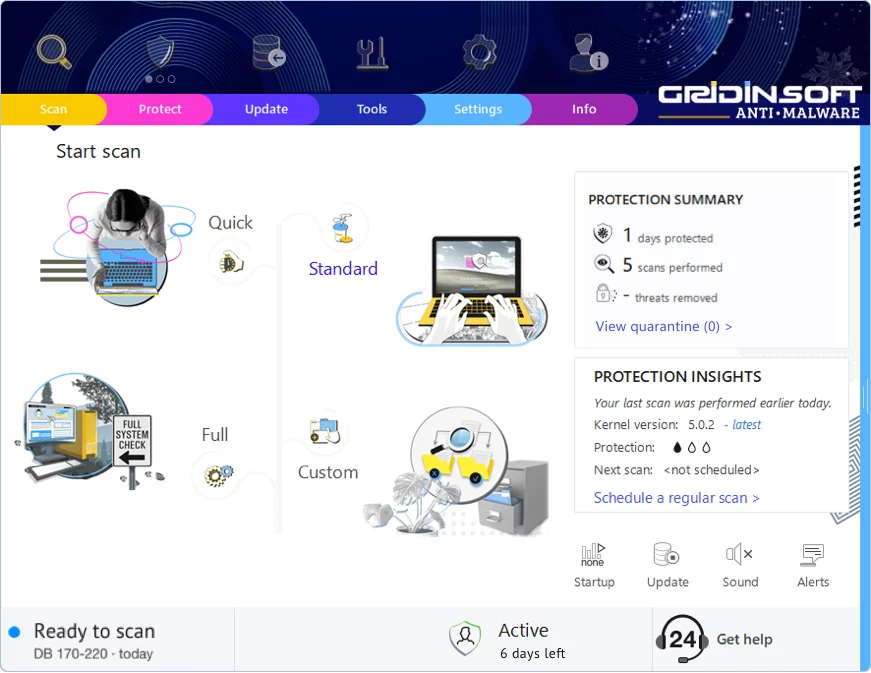
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!