Hyperevade.dll Adware DownWare Analysis
Technical Analysis
| File Name | hyperevade.dll |
| File Type |
PE32+ executable (DLL) (native) x86-64, for MS Windows
|
| Scanner Version | 1.0.254.174 |
| Database Version | 2026-09-12 07:00:18 UTC |
Adware.Win64.DownWare.cl
Malware family: DownWare
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
5bb2caba882ff70025d89b2453dfeb70
|
|
| SHA1 |
7d27161d7ec0afcd52f32aead275e5d12fe904ff
|
|
| SHA256 |
b3dcd78dc2f1482f764a136fa91e836cb3d22eac0d608310f4185e94ec92dcf5
|
|
| SHA512 |
e735b7f7e9692cecb706bdc920f55c3920c76781b52684bc14e5c8806d8fdc2b83452f26303918b77ef3e5b22b1efe0f4e278968baa2de7873ae98962b7d9320
|
PE Analysis
Basic Information
▼| Image Base | 0x180000000 |
| Entry Point | 0x180000000 |
| Compilation Time | 2026-04-14 18:40:58 |
| Checksum | 0x000026e5 (Actual: 0x00001be3) |
| OS Version | 10.0 |
| PEiD Signatures |
PE32+ executable (DLL) (native) x86-64, for MS Windows
|
| Digital Signature | Chain verification from CN=Denuvo GmbH (serial:114358805401419667968931782220079565847, sha1:63421dce069d606d18627cfa9486492bc81f0222) failed: The X.509 certificate provided is self-signed - "Common Name: Denuvo GmbH" |
| Imports | 0 |
| Exports | 10 functions |
| Resources | 0 Resources |
| Sections | 6 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
512 bytes | 512 bytes | 4.59 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
1185A502BE54C9E43AB587F74A9BB854 |
.rdata |
0x00002000 |
1,280 bytes | 1,536 bytes | 0.51 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_READ
|
2A5A2A48F2ED1574E4819838FF7A75B8 |
.data |
0x00003000 |
184 bytes | 512 bytes | 0.14 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
15F524468A4517E767CB77A94E7CF821 |
.pdata |
0x00004000 |
36 bytes | 512 bytes | 0.32 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_READ
|
343302171483E513D22B397E68CD14E0 |
.edata |
0x00005000 |
436 bytes | 512 bytes | 4.39 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
7CAFD03E7DFCD902BE1CFC7DCF7DE1C3 |
.reloc |
0x00006000 |
36 bytes | 512 bytes | 0.50 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
B4E939068BDE4D8093360BAAAA359095 |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
Chain verification from CN=Denuvo GmbH (serial:114358805401419667968931782220079565847, sha1:63421dce069d606d18627cfa9486492bc81f0222) failed: The X.509 certificate provided is self-signed - "Common Name: Denuvo GmbH"
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Adware.Win64.DownWare.cl Removal
Gridinsoft has the capability to identify and eliminate Adware.Win64.DownWare.cl without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
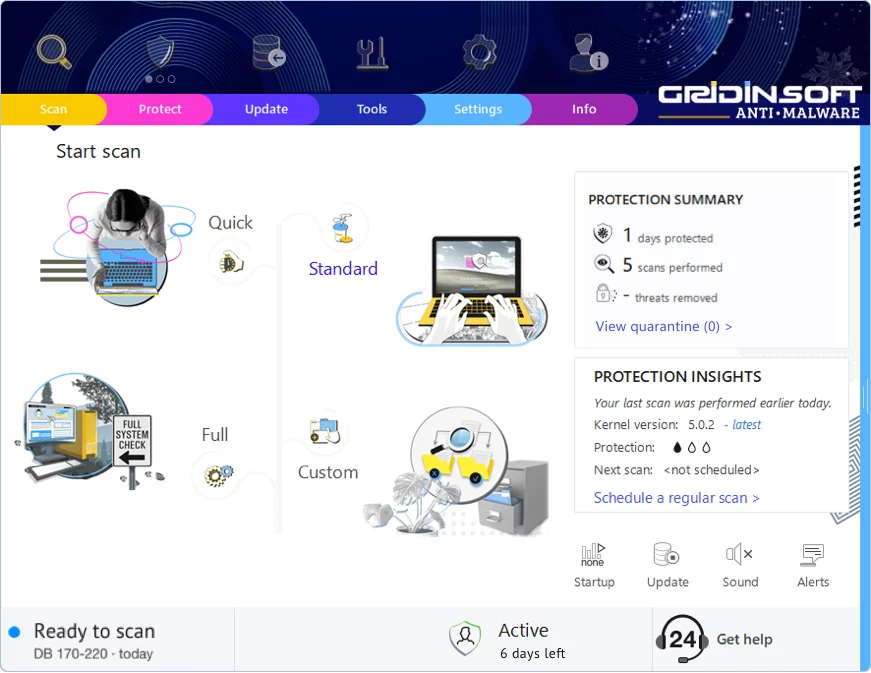
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!