Client-built_protected.exe Stealer Keylogger Analysis
Technical Analysis
| File Name | Client-built_protected.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.214.174 |
| Database Version | 2025-04-16 19:00:17 UTC |
Spy.Win32.Keylogger.dd!n
Malware family: Keylogger
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
f6f7c6ff6c7a9f80d86671f980f7ccf6
|
|
| SHA1 |
8172b4360b319d8d13aa420bc97b6d5bd8b03ff0
|
|
| SHA256 |
92a4a8494eab5704f31ae50c73d17ae577eb312d866342fc67dc52b8e3fae0bf
|
|
| SHA512 |
f296341123468149788f30bb7a34a2a08286369f96003ef8c32528e2d5b845aad809d858f6825cbf96ffc77b8ae1e9fd8917036faa90c1b68ca9d537198d4855
|
|
| ImpHash |
4328f7206db519cd4e82283211d98e83
|
PE Analysis
Basic Information
▼| Image Base | 0x00400000 |
| Entry Point | 0x00912e96 |
| Compilation Time | 2023-03-12 16:16:39 |
| Checksum | 0x008c8469 (Actual: 0x008c8469) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports |
2 libraries
kernel32, mscoree |
| Exports | 0 functions |
| Resources | 2 Resources |
| Sections | 5 Sections |
Version Information
▼| Translation | 0x0000 0x04b0 |
| Comments | |
| CompanyName | |
| FileDescription | Quasar Client |
| FileVersion | 1.4.1 |
| InternalName | Client.exe |
| LegalCopyright | Copyright © MaxXor 2023 |
| LegalTrademarks | |
| OriginalFilename | Client.exe |
| ProductName | Quasar |
| ProductVersion | 1.4.1 |
| Assembly Version | 1.4.1.0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00002000 |
3,268,608 bytes | 3,261,952 bytes | 6.08 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
FE769D33782EC2F5D4C08D75B86A2B11 |
.rsrc |
0x00320000 |
2,707 bytes | 3,072 bytes | 4.65 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
CDEAE95AC72E9E58017D2BCC89D2FBEA |
.reloc |
0x00322000 |
12 bytes | 512 bytes | 0.10 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
280F4C1FAF592077116209D063074F64 |
.idata |
0x00324000 |
8,192 bytes | 512 bytes | 1.14 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
BA1EFBEC90AF71A01F003E00EFF52977 |
.themida |
0x00326000 |
5,939,200 bytes | 5,939,200 bytes | 6.32 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
5D16FAE206047F42B93808A821033AF7 |
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_VERSION | 1 | 796 bytes | |
| RT_MANIFEST | 1 | 1,751 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Spy.Win32.Keylogger.dd!n Removal
Gridinsoft has the capability to identify and eliminate Spy.Win32.Keylogger.dd!n without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
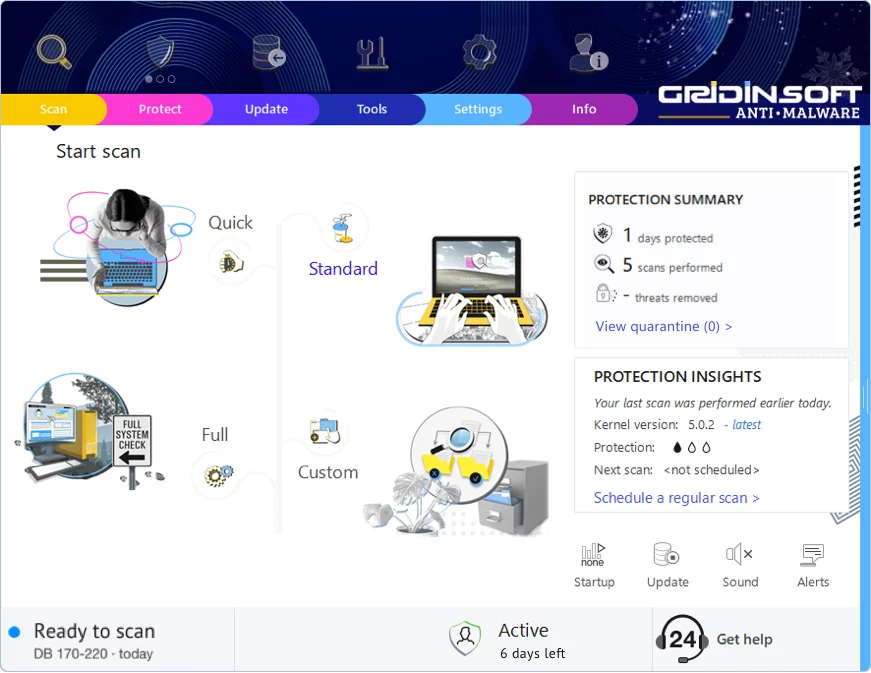
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!