Bad_apple.exe Malware Generic Analysis
Technical Analysis
| File Name | bad_apple.exe |
| File Type |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Scanner Version | 1.0.254.174 |
| Database Version | 2026-09-16 20:01:06 UTC |
Malware.Win64.Generic.cld
Malware family: Generic
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
6a022e937a774f6da038da4634b0fc40
|
|
| SHA1 |
f204d69f3a78629a85f10bd7d2768b6fc3cbd7db
|
|
| SHA256 |
6927cb7245652a3b66f1a4517189c7cd08056875e09e267a29fe13f1d3bd4d1d
|
|
| SHA512 |
752643d0bc50dd82d7cb82dd8e7acea72859a1f57eff9635fcac0950e73bc2fda1228e8e1405a6cc92ea364f8026e24f4fb88d55f5e92bfe82214dffbe76ca4d
|
|
| ImpHash |
30f731cca9cc3ab87b86f180728ab4b5
|
PE Analysis
Basic Information
▼| Icon |
Hash: da87120a550b8ff7b36f8b69c6343ec1
Fuzzy: 5dea1b09f6acc48bcdf918ba0ef2339a dHash: 10d0c8f898b8b8e0 |
| Image Base | 0x140000000 |
| Entry Point | 0x14006e080 |
| Compilation Time | 2023-07-31 12:08:33 |
| Checksum | 0x00000000 (Actual: 0x004d48fc) |
| OS Version | 6.0 |
| PEiD Signatures |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 14 libraries |
| Exports | 0 functions |
| Resources | 8 Resources |
| Sections | 6 Sections |
Version Information
▼| FileVersion | 0.1.0 |
| FileDescription | badapple |
| CompanyName | https://github.com/mon |
| ProductVersion | 0.1.0 |
| Translation | 0x0000 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
461,583 bytes | 461,824 bytes | 6.36 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
B9EC0D2967C7901CA8040E079406140F |
.rdata |
0x00072000 |
4,493,294 bytes | 4,493,312 bytes | 7.85 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
ED23791DDD9D31E4A720C385B1451B76 |
.data |
0x004bb000 |
525,224 bytes | 512 bytes | 1.62 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
20915ADF683C7322891EFBDF7062B732 |
.pdata |
0x0053c000 |
13,560 bytes | 13,824 bytes | 5.69 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
C3F754145DB1DC42FCAA239C2CFACE50 |
.rsrc |
0x00540000 |
87,776 bytes | 88,064 bytes | 7.64 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
7785BDE51BEF6668AE3F113B01620A93 |
.reloc |
0x00556000 |
3,720 bytes | 4,096 bytes | 5.25 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
0569B1A2B5386226D4D9D554B986C5A0 |
Entropy Analysis Alert
2 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 5 | 86,397 bytes | |
| RT_GROUP_ICON | 1 | 76 bytes | |
| RT_VERSION | 1 | 452 bytes | |
| RT_MANIFEST | 1 | 338 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Malware.Win64.Generic.cld Removal
Gridinsoft has the capability to identify and eliminate Malware.Win64.Generic.cld without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
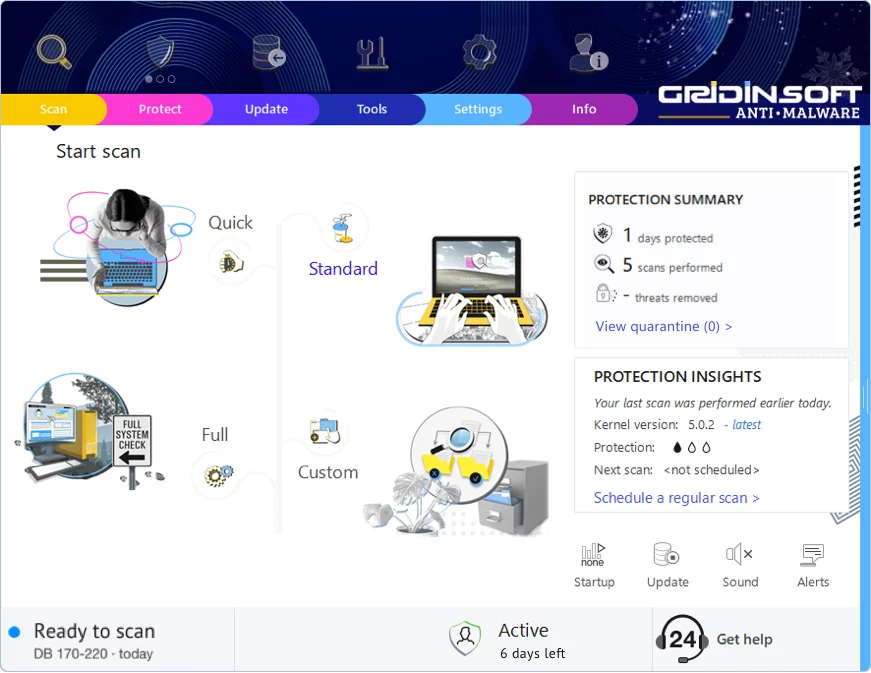
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!