ArmorPaint.exe Trojan Heuristic Analysis
Technical Analysis
| File Name | ArmorPaint.exe |
| File Type |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Scanner Version | 1.0.254.174 |
| Database Version | 2026-09-21 16:01:28 UTC |
Trojan.Heur!.02812023
Malware family: Heuristic
Scan Another File
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
e57779f926f93ecc49af8213e257680a
|
|
| SHA1 |
b8185e3783175f549bcbaa6ebc66d32c76184f77
|
|
| SHA256 |
561b717d57f581bc65e9bd238aec113cbbd8d6bf90691338dd6b64f0f3590552
|
|
| SHA512 |
ffa760d31a02af2045923e0021610efd712c611277afd96e7436acb8467124e0650bc09a9c8aa1e54a8857498317450948cd5b3effc375ed4764dbb9761a1b5c
|
|
| ImpHash |
4204f9d5d655b10c18bd0607ba9318dd
|
PE Analysis
Basic Information
▼| Icon |
Hash: 94b07d20f41e0d5ccb5ea504bedc427e
Fuzzy: ecf5e1d5c45877575abfcaac971bc621 dHash: 2cd2d269ad4c1609 |
| Image Base | 0x140000000 |
| Entry Point | 0x140235c30 |
| Compilation Time | 2026-09-08 02:15:25 |
| Checksum | 0x00000000 (Actual: 0x0030a7bf) |
| OS Version | 6.0 |
| PEiD Signatures |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 11 libraries |
| Exports | 0 functions |
| Resources | 7 Resources |
| Sections | 8 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
2,513,478 bytes | 2,513,920 bytes | 6.53 (Compressed) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
34ADA81B5BE995A90C6D70638091F8E9 |
.rdata |
0x00267000 |
410,556 bytes | 410,624 bytes | 6.05 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
6BBF19CFDE7C2C532210C9F106539C38 |
.data |
0x002cc000 |
91,916,420 bytes | 144,384 bytes | 5.35 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
E867B5E027D09310A589D023ACAA3436 |
.pdata |
0x05a75000 |
46,092 bytes | 46,592 bytes | 5.97 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
4794CBDAA4F950A51014E57E70812CB9 |
.fptable |
0x05a81000 |
256 bytes | 512 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
BF619EAC0CDF3F68D496EA9344137E8B |
_RDATA |
0x05a82000 |
1,092 bytes | 1,536 bytes | 2.97 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
4BAE5DFE86A1E818EAD639A46E964329 |
.rsrc |
0x05a83000 |
10,896 bytes | 11,264 bytes | 7.46 (Compressed) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
A3778AB6F981B007007DD2FA947365FD |
.reloc |
0x05a86000 |
7,604 bytes | 7,680 bytes | 5.44 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
BEA6D1EA8A056CE6C53FD7515F4BFCA1 |
Entropy Analysis Alert
2 section(s) with elevated entropy (≥6.5) - possible compression
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 5 | 9,548 bytes | |
| RT_GROUP_ICON | 1 | 76 bytes | |
| RT_MANIFEST | 1 | 820 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Trojan.Heur!.02812023 Removal
Gridinsoft has the capability to identify and eliminate Trojan.Heur!.02812023 without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
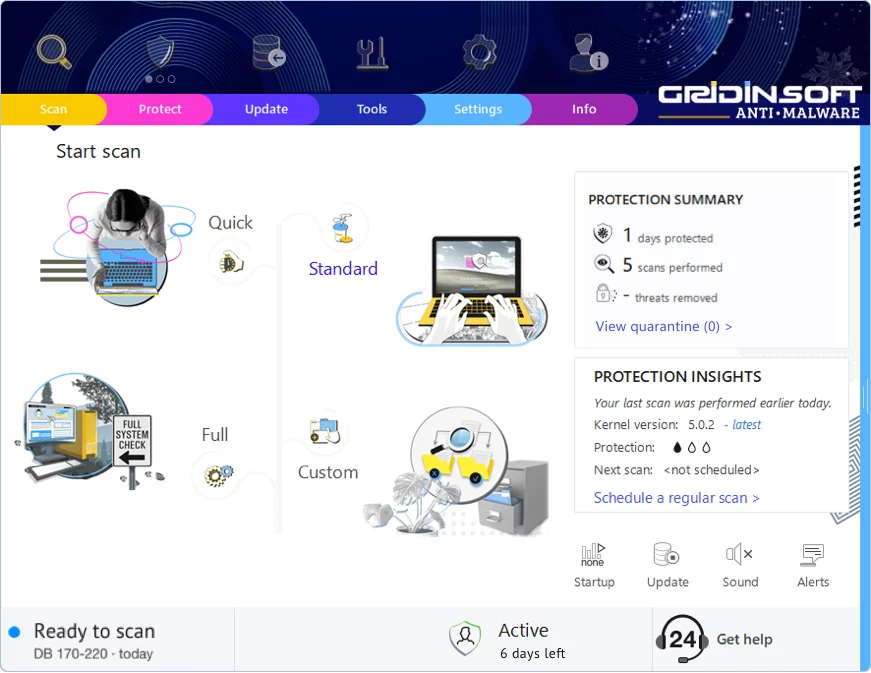
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment

Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!