动漫共和国概念版-1.4.4-flutter-setup-x64.exe Adware Gen Analysis
Technical Analysis
| File Name | 动漫共和国概念版-1.4.4-flutter-setup-x64.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archive
|
| Scanner Version | 1.0.256.174 |
| Database Version | 2026-10-03 07:07:03 UTC |
Adware.Win32.Gen.cl
Malware family: Gen
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
d8a3ad103e90e31290ae6816850e404f
|
|
| SHA1 |
4b0d38b5d6a9a2e6bfad1bb3b3038eb26ad3c43f
|
|
| SHA256 |
c1ca50dc18d11751a1dd5979c77d809c452fa4ded264189bdf5ce8e7c706695f
|
|
| SHA512 |
9885cdba7f03426fb79cbfc0149577d2f6683f58ebaf7386f2dc7b1ed48cf087024d5b0e4e96dbfe4a5d4c5483d37bd9ab42feb1f750fb6be6e092c5d4e40ed1
|
|
| ImpHash |
46ce5c12b293febbeb513b196aa7f843
|
PE Analysis
Basic Information
▼| Icon |
Hash: a8adc1ce024bc42a7a3f3fb4ca6a1adc
Fuzzy: b475db0d94ee5edc026474d8575bd07f dHash: 5572335451f0d461 |
| Image Base | 0x00400000 |
| Entry Point | 0x0040369f |
| Compilation Time | 2025-03-08 23:05:20 |
| Checksum | 0x00000000 (Actual: 0x01b26763) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archive
|
| Digital Signature | No valid SignedData structure was found. |
| Imports |
7 libraries
ADVAPI32, SHELL32, ole32, COMCTL32, USER32, GDI32, KERNEL32 |
| Exports | 0 functions |
| Resources | 9 Resources |
| Sections | 5 Sections |
Version Information
▼| CompanyName | 动漫共和国 |
| FileDescription | 动漫共和国概念版 安装程序 |
| FileVersion | 1.4.4.144 |
| LegalCopyright | Copyright (C) 2026 动漫共和国. All rights reserved. |
| ProductName | 动漫共和国概念版 |
| ProductVersion | 1.4.4.144 |
| Translation | 0x0804 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
26,385 bytes | 26,624 bytes | 6.45 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
AFB6C5993570F82E85EC446BBB886505 |
.rdata |
0x00008000 |
4,952 bytes | 5,120 bytes | 5.10 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
E913094D8CCEACA6B405BBBB52936387 |
.data |
0x0000a000 |
129,912 bytes | 1,536 bytes | 4.12 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
9D011BEBA2FE64A93F62FBB227CC9C35 |
.ndata |
0x0002a000 |
155,648 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_UNINITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
D41D8CD98F00B204E9800998ECF8427E |
.rsrc |
0x00050000 |
84,592 bytes | 84,992 bytes | 7.94 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
590B574AC751152D17B61DF403B3D8C3 |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 1 | 80,746 bytes | |
| RT_DIALOG | 5 | 1,348 bytes | |
| RT_GROUP_ICON | 1 | 20 bytes | |
| RT_VERSION | 1 | 624 bytes | |
| RT_MANIFEST | 1 | 1,249 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Adware.Win32.Gen.cl Removal
Gridinsoft has the capability to identify and eliminate Adware.Win32.Gen.cl without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
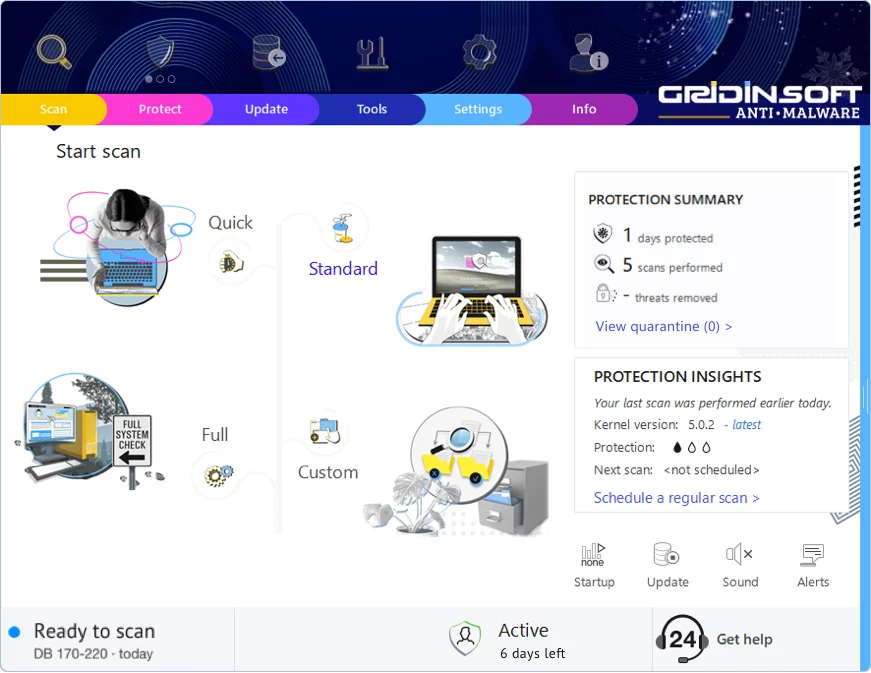
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!