WinToolsNet.exe Trojan Agent Analysis
Technical Analysis
| File Name | WinToolsNet.exe |
| File Type |
MS-DOS executable PE32 executable (GUI) Intel 80386 (stripped to external PDB), for MS Windows, MZ for MS-DOS
|
| Scanner Version | 1.0.257.174 |
| Database Version | 2026-10-18 19:07:03 UTC |
Trojan.Win32.Agent.sa
Malware family: Agent
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
a0946250850516f494cbfd43c2b2b9db
|
|
| SHA1 |
6189ac9acd8800211d20eaced2bfc8368ff3d8ee
|
|
| SHA256 |
ba38be61a59e64b9462b7db2985951fb33853e1ea97263d37d0c7e475a5ea6cc
|
|
| SHA512 |
9e7cfcafff000f32483483b2f23c0586ea25977fec42581a447e64d68eb74bdb0911e410b624dec02d8bce2d18ee00e89619df9e61c14a0a477de5de9d11a476
|
|
| ImpHash |
fa2c9800f6817f3d4350be2e4dbbfa57
|
PE Analysis
Basic Information
▼| Icon |
Hash: b5f7819a0cff11f058e7453a087b55d8
Fuzzy: 5407546b8f1a048230a38b45bbe5dcc4 dHash: 38f4f0b08acc7a38 |
| Image Base | 0x00400000 |
| Entry Point | 0x00926291 |
| Compilation Time | 2026-10-12 15:31:34 |
| Checksum | 0x00000000 (Actual: 0x002c8801) |
| OS Version | 5.1 |
| PEiD Signatures |
MS-DOS executable PE32 executable (GUI) Intel 80386 (stripped to external PDB), for MS Windows, MZ for MS-DOS
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 11 libraries |
| Exports | 0 functions |
| Resources | 659 Resources |
| Sections | 3 Sections |
Version Information
▼| CompanyName | WinTools Software, Ltd. |
| FileDescription | WinTools.net - Windows System Optimization Suite |
| FileVersion | 26.10.1.0 |
| InternalName | WinTools.net® |
| LegalCopyright | Copyright © 2002–2026 All rights reserved. |
| LegalTrademarks | https://www.wintools.net |
| OriginalFilename | WINTOOLSNET.EXE |
| ProductName | WinTools.net |
| ProductVersion | 26.10.1.0 |
| Comments | CEO Ruslan Smekalov |
| Translation | 0x0009 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
|
0x00001000 |
5,394,432 bytes | 480,256 bytes | 8.00 (Packed/Encrypted) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_CNT_UNINITIALIZED_DATA|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
FBC7015E825820614EBC90992647E285 |
|
0x00526000 |
3,579 bytes | 3,584 bytes | 6.03 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_CNT_UNINITIALIZED_DATA|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
2C55BE57427D5AE3F6FC67FC6C6866E5 |
.rsrc |
0x00527000 |
2,394,464 bytes | 2,394,624 bytes | 4.50 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
9C3E5965DE31DA6348220EB61103BBAF |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_BITMAP | 70 | 2,037,106 bytes | |
| RT_ICON | 287 | 2,354,729 bytes | |
| RT_DIALOG | 17 | 6,234 bytes | |
| RT_STRING | 2 | 426 bytes | |
| RT_ACCELERATOR | 1 | 200 bytes | |
| RT_GROUP_ICON | 280 | 5,698 bytes | |
| RT_VERSION | 1 | 1,020 bytes | |
| RT_MANIFEST | 1 | 771 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Trojan.Win32.Agent.sa Removal
Gridinsoft has the capability to identify and eliminate Trojan.Win32.Agent.sa without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
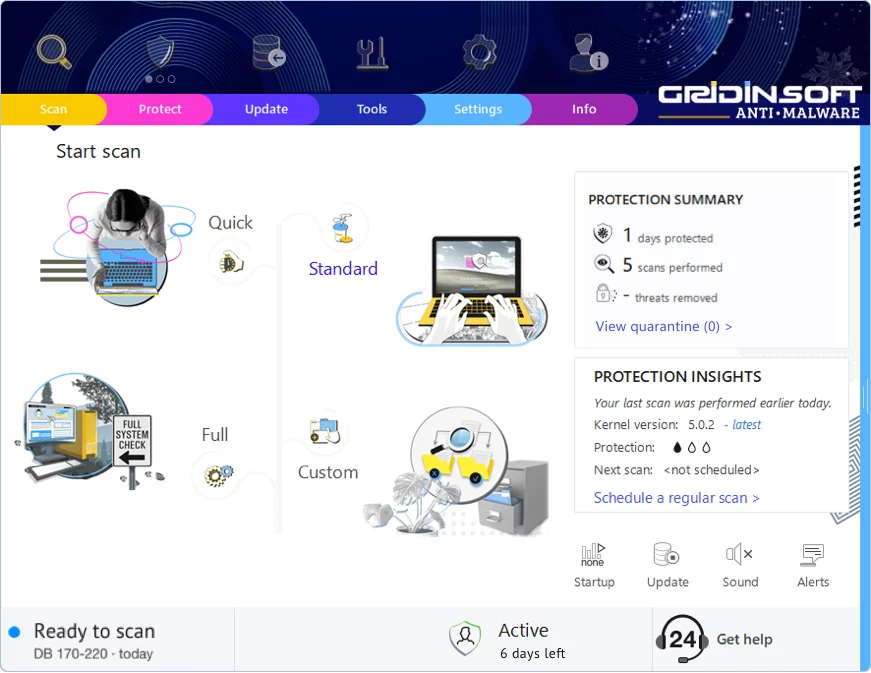
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!