RUNE64.dll Trojan Heuristic Analysis
Technical Analysis
| File Name | RUNE64.dll |
| File Type |
PE32+ executable (DLL) (GUI) x86-64, for MS Windows
|
| Scanner Version | 1.0.253.174 |
| Database Version | 2026-08-29 15:00:18 UTC |
Trojan.Heur!.022120A2
Malware family: Heuristic
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
0c415a22227d44f111e30371a4028c08
|
|
| SHA1 |
2bc89dddf012eaf7d73aa52b9458074307337da3
|
|
| SHA256 |
a184efddc60f12f159131c1a49662460ea766b1d0960423df723ad984d966d6b
|
|
| SHA512 |
ff2209530ceb3e2b52c2127f78910fc5516fb1b8d2ae0742323361a1988dc6ae2f2bcd86386a7a82e22549922121a2c743d3d4d1e15efbc962854a33d0a70d8d
|
|
| ImpHash |
bbbce18a0db7f3fb0836eae760f4efbb
|
PE Analysis
Basic Information
▼| Image Base | 0x180000000 |
| Entry Point | 0x1808a61a7 |
| Compilation Time | 2025-03-04 21:45:25 |
| Checksum | 0x00000000 (Actual: 0x00b2c181) |
| OS Version | 6.0 |
| PEiD Signatures |
PE32+ executable (DLL) (GUI) x86-64, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports |
2 libraries
KERNEL32, USER32 |
| Exports | 1 functions |
| Resources | 0 Resources |
| Sections | 9 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
1,943,600 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.rdata |
0x001dc000 |
515,242 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.data |
0x0025a000 |
72,360 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
D41D8CD98F00B204E9800998ECF8427E |
.pdata |
0x0026c000 |
54,648 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.fptable |
0x0027a000 |
256 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
D41D8CD98F00B204E9800998ECF8427E |
.rune0 |
0x0027b000 |
6,342,604 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.rune1 |
0x00888000 |
88 bytes | 512 bytes | 0.14 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
066135760E26C27093C905F753EAD738 |
.rune2 |
0x00889000 |
11,664,868 bytes | 11,664,896 bytes | 7.79 (Packed/Encrypted) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
69EF74E0E01306004E4B629929B4929A |
.reloc |
0x013a9000 |
296 bytes | 512 bytes | 2.78 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
FEC00963E00C53302E11C00BD095E5FB |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Trojan.Heur!.022120A2 Removal
Gridinsoft has the capability to identify and eliminate Trojan.Heur!.022120A2 without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
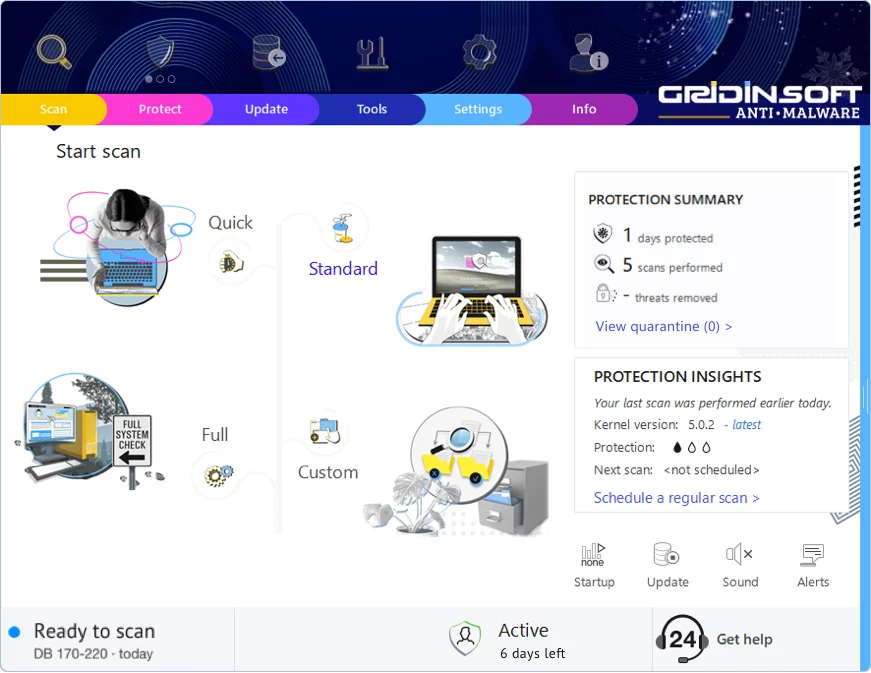
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!