HAKI - Temp spoofer.exe Trojan Heuristic Analysis
Technical Analysis
| File Name | HAKI - Temp spoofer.exe |
| File Type |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Scanner Version | 1.0.259.174 |
| Database Version | 2026-11-07 22:07:02 UTC |
Trojan.Heur!.02212023
Malware family: Heuristic
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
fea36853dc9ba0063fb7359b9a53cd0d
|
|
| SHA1 |
ebe26a83ede484ef16e62e0c1faa41b01352f307
|
|
| SHA256 |
a14410398c1d28eea2825c9bba401e8a31f72fc1127a796091e5af73cacbde59
|
|
| SHA512 |
fc1a6e1492244536e5fd1618911cc6769ee0f2f1686c3bcc3b16a408c1f5449338acf8dff56964c175d137309c4a38af54d19e9f529697f13288ba14cc42e099
|
|
| ImpHash |
8d8a968df4e2c620eaff9b3de53c8742
|
PE Analysis
Basic Information
▼| Image Base | 0x140000000 |
| Entry Point | 0x140e2d73d |
| Compilation Time | 2026-10-28 22:09:40 |
| Checksum | 0x00000000 (Actual: 0x01521c19) |
| OS Version | 6.0 |
| PEiD Signatures |
PE32+ executable (GUI) x86-64, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports | 21 libraries |
| Exports | 0 functions |
| Resources | 1 Resources |
| Sections | 8 Sections |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
338,196 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.rdata |
0x00054000 |
1,050,258 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.data |
0x00155000 |
2,504 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
D41D8CD98F00B204E9800998ECF8427E |
.pdata |
0x00156000 |
15,216 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.meow0 |
0x0015a000 |
13,049,371 bytes | 0 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
D41D8CD98F00B204E9800998ECF8427E |
.meow1 |
0x00dcc000 |
400 bytes | 512 bytes | 1.36 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
F3DDE05B49C3C5890F0BEA2F41469C96 |
.meow2 |
0x00dcd000 |
22,120,364 bytes | 22,120,448 bytes | 7.72 (Packed/Encrypted) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_NOT_PAGED|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
7353B1EF6AAA32989D48269225396655 |
.rsrc |
0x022e6000 |
480 bytes | 512 bytes | 4.78 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
55004C59FDB5C90F4760FDBF50F25682 |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_MANIFEST | 1 | 392 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Trojan.Heur!.02212023 Removal
Gridinsoft has the capability to identify and eliminate Trojan.Heur!.02212023 without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
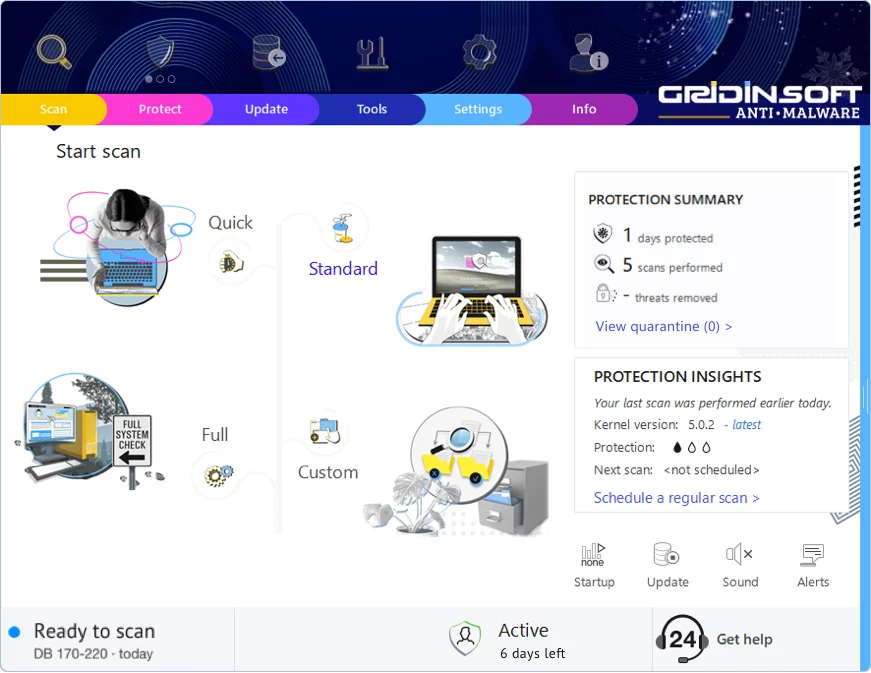
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!