GTA V Save Editor - Installer.exe Malware Generic Analysis
Technical Analysis
| File Name | GTA V Save Editor - Installer.exe |
| File Type |
PE32 executable (GUI) Intel 80386 Mono/.Net assembly, for MS Windows
|
| Scanner Version | 1.0.258.174 |
| Database Version | 2026-11-01 01:07:02 UTC |
Malware.Win32.Generic.cld
Malware family: Generic
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
c439b3e7e94942d98aa6ce60f38cb0eb
|
|
| SHA1 |
84342ced50191a89d4d6e350fb3d53120b19f7db
|
|
| SHA256 |
63dfbadcd31818a9f1e388b48710ebebec03ea801feef7c5a850fb6a73672d29
|
|
| SHA512 |
1d6d233b9f3a0940729fb273c995013f38dae43c6bdfcc0b712327378654ee7fe53a6c95000853a8beb9e5c1f86fc245436f1bb8ea95bacf08bd6d84f4246344
|
|
| ImpHash |
f34d5f2d4577ed6d9ceec516c1f5a744
|
PE Analysis
Basic Information
▼| Icon |
Hash: 781fc359136ef120a7d6f7874088d175
Fuzzy: 3777e0f0de24e75dda4bcb33a026fb08 dHash: b3b2f6fc6968b230 |
| Image Base | 0x00400000 |
| Entry Point | 0x02487a16 |
| Compilation Time | 2025-12-29 05:08:49 |
| Checksum | 0x00000000 (Actual: 0x020a421f) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386 Mono/.Net assembly, for MS Windows
|
| PDB Path | C:\Users\XB36Hazard\Documents\Visual Studio 2019\Projects\GTAV_Prerequisite\GTAVSaveEditor_Prerequisite\obj\Release\GTA V Save Editor - Installer.pdb |
| Digital Signature | No valid SignedData structure was found. |
| Imports |
1 libraries
mscoree |
| Exports | 0 functions |
| Resources | 4 Resources |
| Sections | 3 Sections |
Version Information
▼| Translation | 0x0000 0x04b0 |
| Comments | Installs GTA V Save Editor prerequisite files |
| CompanyName | XB36Hazard |
| FileDescription | GTA V Save Editor - Installer |
| FileVersion | 5.9.0.0 |
| InternalName | GTA V Save Editor - Installer.exe |
| LegalCopyright | Copyright © XB36Hazard 2025 |
| LegalTrademarks | XB36Hazard |
| OriginalFilename | GTA V Save Editor - Installer.exe |
| ProductName | GTA V Save Editor - Installer |
| ProductVersion | 5.9.0.0 |
| Assembly Version | 5.9.0.0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00002000 |
34,101,788 bytes | 34,102,272 bytes | 8.00 (Packed/Encrypted) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
8B629F556ADD42064028F3489E8791BE |
.reloc |
0x02088000 |
12 bytes | 512 bytes | 0.12 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
81B4A91D1E2B69CFE2F195BF4217AEE9 |
.rsrc |
0x0208a000 |
58,016 bytes | 58,368 bytes | 7.93 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
AF84DF5B420C6603C3E2356A2B89066C |
Entropy Analysis Alert
2 section(s) with high entropy (≥7.5) detected - possible packing/encryption
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 1 | 53,177 bytes | |
| RT_GROUP_ICON | 1 | 20 bytes | |
| RT_VERSION | 1 | 1,104 bytes | |
| RT_MANIFEST | 1 | 3,408 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Malware.Win32.Generic.cld Removal
Gridinsoft has the capability to identify and eliminate Malware.Win32.Generic.cld without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
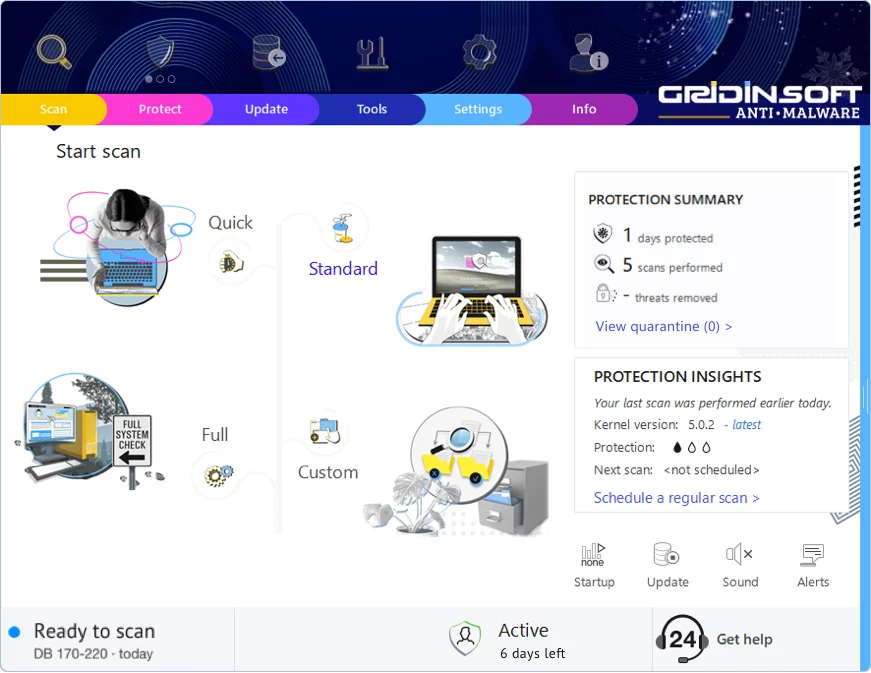
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!