Limewire18c.exe Adware Agent Analysis
Technical Analysis
| File Name | limewire18c.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.258.174 |
| Database Version | 2026-10-30 18:07:02 UTC |
Adware.Win32.Agent.cld
Malware family: Agent
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
fee8881e78392d895a00bb75e0101b06
|
|
| SHA1 |
aaddd32d11508c74637f5704d55245df9f7e4750
|
|
| SHA256 |
20fdd75142ff189a68efd246e5fa663c1db2d03c323220f37b88a2048359bd14
|
|
| SHA512 |
30af98a1f137b8a1b493f38c259249bd4001ad105e97d38e4a6f6b55406006f7ee04f8b7f8defaac5fe98271707909cc567140c30a86f4d1ed3377a994fb4563
|
|
| ImpHash |
ba1b8fbc2b1c93935a67fb0c7432f51b
|
PE Analysis
Basic Information
▼| Icon |
Hash: b8a4c86f4b6ae0d00860dfb762aff30d
Fuzzy: e86457f73bcdf352ccf7af9e6dcac0b7 dHash: c8949c8de6b2aec6 |
| Image Base | 0x00400000 |
| Entry Point | 0x00412642 |
| Compilation Time | 2001-10-15 22:33:34 |
| Checksum | 0x00000000 (Actual: 0x003d4e87) |
| OS Version | 4.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Digital Signature | No valid SignedData structure was found. |
| Imports |
9 libraries
VERSION, SHELL32, COMCTL32, KERNEL32, USER32, GDI32, ADVAPI32, ole32, OLEAUT32 |
| Exports | 0 functions |
| Resources | 24 Resources |
| Sections | 4 Sections |
Version Information
▼| Comments | |
| CompanyName | LimeWire |
| FileDescription | Setup Launcher |
| FileVersion | 1.82 |
| LegalCopyright | 747 |
| ProductName | LimeWire 1.8c |
| ProductVersion | 1.82 |
| Translation | 0x0409 0x04e4 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
106,598 bytes | 110,592 bytes | 6.44 (Normal) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
E565A3BD43F048F843AE89252AA444B4 |
.rdata |
0x0001c000 |
13,550 bytes | 16,384 bytes | 4.81 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
64E67473BE916C9D6526E6CE5C37091B |
.data |
0x00020000 |
29,944 bytes | 20,480 bytes | 2.42 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
E779C58161DA7DEFA307AAAF0247AC7D |
.rsrc |
0x00028000 |
46,632 bytes | 49,152 bytes | 7.11 (Compressed) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
DD1C9CD5D21588539E9E448C16A966FB |
Entropy Analysis Alert
1 section(s) with elevated entropy (≥6.5) - possible compression
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| GIF | 1 | 31,466 bytes | |
| RT_CURSOR | 1 | 308 bytes | |
| RT_ICON | 9 | 10,024 bytes | |
| RT_DIALOG | 5 | 1,490 bytes | |
| RT_STRING | 3 | 424 bytes | |
| RT_GROUP_CURSOR | 1 | 20 bytes | |
| RT_GROUP_ICON | 3 | 144 bytes | |
| RT_VERSION | 1 | 1,320 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Adware.Win32.Agent.cld Removal
Gridinsoft has the capability to identify and eliminate Adware.Win32.Agent.cld without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
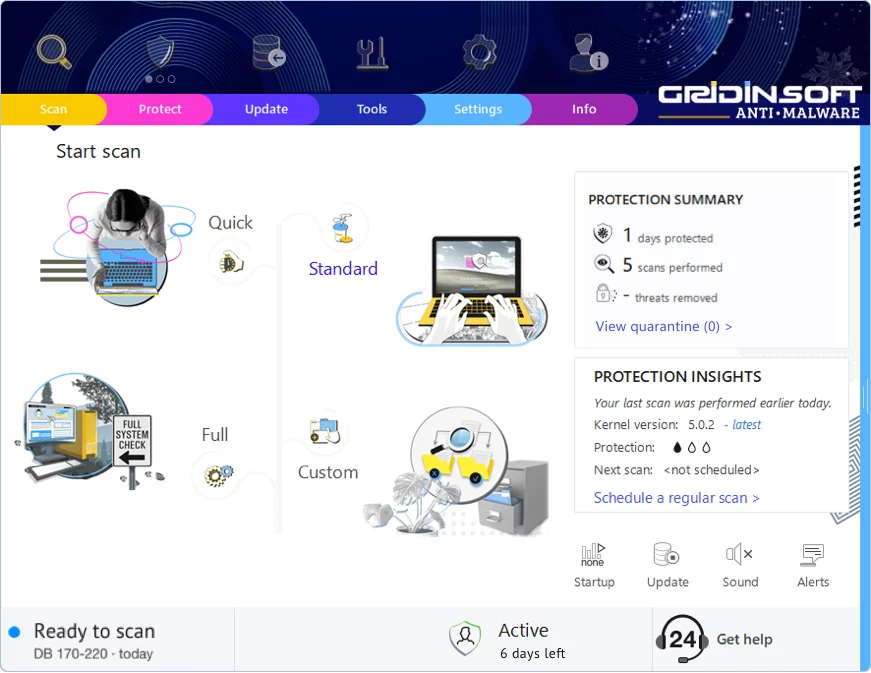
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!