TriarchLauncher.exe Malware Generic Analysis
Technical Analysis
| File Name | TriarchLauncher.exe |
| File Type |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| Scanner Version | 1.0.257.174 |
| Database Version | 2026-10-12 06:07:02 UTC |
Malware.Win32.Generic.cld
Malware family: Generic
Scan Another File
The uploaded file itself is not retained or shared with third parties. File names, hashes, and analysis results may appear in public reports. For confidential material, contact Support before uploading. How we use your data.
File Identification
| Hash Type | Value | Action |
|---|---|---|
| MD5 |
707b394b9fe617f07cd52b893eebbd52
|
|
| SHA1 |
b83d8155b9852d26285a45bd15e82f277ece7212
|
|
| SHA256 |
03766b9f9b74e6426f0204c8954d7f882dee17c03988a4eb47648ef714f1ee01
|
|
| SHA512 |
a1b70c529769a8196da0aa19d2f28208aeb22e96f2f0ba0fa9f419a29c60b7998240961fe109e52b692383e0c118cca2e2c86ffd454ba385f0a1616603599c38
|
|
| ImpHash |
6253a3b40fe63c8b5089403c598adbff
|
PE Analysis
Basic Information
▼| Icon |
Hash: 887a6c58ad2c70adf1998e6a533db2f9
Fuzzy: f3b817005de42cc0c55c7bcd153d3b80 dHash: 70d4d4f232a47270 |
| Image Base | 0x00400000 |
| Entry Point | 0x0042f3ea |
| Compilation Time | 2026-08-23 19:42:55 |
| Checksum | 0x00000000 (Actual: 0x0008183d) |
| OS Version | 6.0 |
| PEiD Signatures |
PE32 executable (GUI) Intel 80386, for MS Windows
|
| PDB Path | %%%TriarchLauncher.pdb%%% |
| Digital Signature | No valid SignedData structure was found. |
| Imports |
8 libraries
WININET, urlmon, USER32, GDI32, SHELL32, ADVAPI32, ole32, KERNEL32 |
| Exports | 0 functions |
| Resources | 4 Resources |
| Sections | 6 Sections |
Version Information
▼| CompanyName | Triarch Online |
| FileDescription | Triarch Online Launcher |
| FileVersion | 1.0.1.0 |
| InternalName | TriarchLauncher |
| LegalCopyright | Copyright (C) 2026 Triarch Online |
| OriginalFilename | TriarchLauncher.exe |
| ProductName | Triarch Online |
| ProductVersion | 1.0.1.0 |
| Translation | 0x0409 0x04b0 |
PE Sections
▼| Name | Virtual Address | Virtual Size | Raw Size | Entropy | Characteristics | MD5 |
|---|---|---|---|---|---|---|
.text |
0x00001000 |
336,205 bytes | 336,384 bytes | 6.65 (Compressed) |
IMAGE_SCN_CNT_CODE|IMAGE_SCN_MEM_EXECUTE|IMAGE_SCN_MEM_READ
|
D8817F79DD8B16BE2C0990A110171CAE |
.rdata |
0x00054000 |
134,746 bytes | 135,168 bytes | 5.97 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
4CFB8AEB137C84C679F25AB07B1574A5 |
.data |
0x00075000 |
16,628 bytes | 8,704 bytes | 4.16 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
2B88FA33BE17F4EE6F1BCEF68C2E7072 |
.fptable |
0x0007a000 |
128 bytes | 512 bytes | 0.00 (Normal) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ|IMAGE_SCN_MEM_WRITE
|
BF619EAC0CDF3F68D496EA9344137E8B |
.rsrc |
0x0007b000 |
33,440 bytes | 33,792 bytes | 7.92 (Packed/Encrypted) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_READ
|
C05E3BC70CE9D3D0644718E8B24C377C |
.reloc |
0x00084000 |
13,972 bytes | 14,336 bytes | 6.58 (Compressed) |
IMAGE_SCN_CNT_INITIALIZED_DATA|IMAGE_SCN_MEM_DISCARDABLE|IMAGE_SCN_MEM_READ
|
46440F4D4E9BF2BA8584CD829B501512 |
Entropy Analysis Alert
1 section(s) with high entropy (≥7.5) detected - possible packing/encryption
2 section(s) with elevated entropy (≥6.5) - possible compression
Resource Analysis
▼| Resource Type | Count | Total Size | Percentage |
|---|---|---|---|
| RT_ICON | 1 | 31,938 bytes | |
| RT_GROUP_ICON | 1 | 20 bytes | |
| RT_VERSION | 1 | 784 bytes | |
| RT_MANIFEST | 1 | 381 bytes |
Certificate Chain Analysis
▼No Digital Signatures
This file is not digitally signed.
Security Implications:
- Cannot verify the publisher's identity
- Increased security risk when running this file
- May trigger security warnings on some systems
⚠ This file either lacks a digital signature or the certificate chain could not be verified
Exercise caution when executing unsigned files from unknown sources
Certificate Verification Status
No valid SignedData structure was found.
Recommendation: Verify the file source and ensure it comes from a trusted publisher.
Malware.Win32.Generic.cld Removal
Gridinsoft has the capability to identify and eliminate Malware.Win32.Generic.cld without requiring further user intervention.
Download Anti-MalwareRemoval Instructions
Follow these steps to completely remove the threat from your system
-
1
Get Gridinsoft Anti-Malware — it's a quick 2 MB download that won't slow down your PC.
-
2
Run the installer gsam-en-install.exe. The setup takes about 2 minutes and doesn't require a restart.
-
3
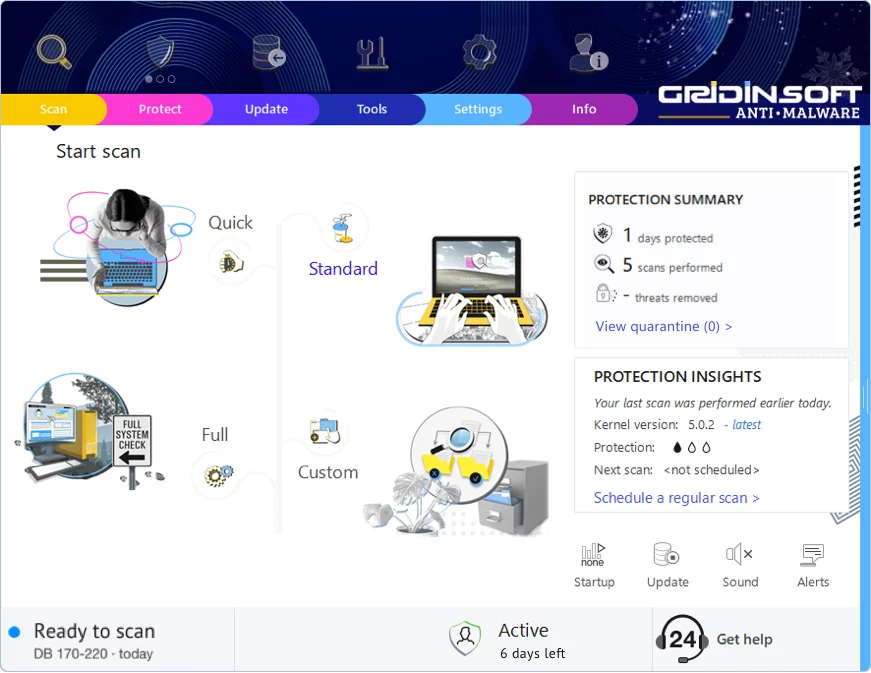
The app launches right after installation. You'll see the main dashboard with the scan button front and center.
-
4
Hit "Standard Scan" — this checks all the spots where malware typically hides: temp folders, browser data, startup programs, and system directories.
-
5
Once the scan finds this threat, click "Clean Now". The removal usually happens instantly, though some stubborn infections may need a reboot.
-
6
If you see a restart prompt, go ahead and reboot. This clears any malware that was running in memory and ensures your system starts fresh.
Leave a Comment
Gridinsoft Anti-Malware
Stay Malware-Free: Keep Your PC Protected with Gridinsoft Anti-Malware
Gridinsoft Anti-Malware offers just that—peace of mind with a robust, user-friendly solution that’s constantly updated to combat the latest threats. Designed by cybersecurity experts, it provides real-time protection and effortless malware removal. It’s not just about detecting threats; it's about enhancing your digital life with uninterrupted security. Give it a try and experience what it feels like to browse worry-free!