
What Gridinsoft observed on glacat.com
A Gridinsoft threat analyst reviewed the site directly and documented the evidence behind this decision.
GMA-20261021151406-031cbace
- Reviewed
- by Gridinsoft Threat Analyst
- Analyst finding
- Public URL Shortener and File-Sharing Service — Exact-Object Review Required
- Evidence basis
- First-party site analysis External vendor intelligence: Context only — not used for this decision
The independent current review did not reproduce an active phishing or malware object on glacat.com. The fresh Gridinsoft result named no concrete harmful object, the reviewed root and public pages showed the declared shortening and sharing service, and all twenty-eight exact public short codes found through public intelligence currently returned HTTP 404 without a redirect. Public urlscan records did preserve historical exact codes redirecting to unrelated payment- or brand-like paths, which establishes past object-level redirect abuse, but the available captures did not expose a specific credential receiver, malware payload, file, or hash. External domain blacklist labels and retained OTX relations remain context and do not identify a current sample. A domain-wide Safe conclusion is not warranted because the complete live, private, unindexed, deleted, and future user-controlled namespace cannot be enumerated. The existing Suspicious Website classification is compatible with this inconclusive exact-object-dependent result, so no classification change is supported.
Analyst findings
Review 8 documented observations View evidence
A fresh supported Gridinsoft result for glacat.com reached the service root over HTTP 200 and exposed no positive behavior signal. The result did not identify an exact credential receiver, unrelated redirect, automatic download, malware file, payload, exploit, command, or hash. Its Suspicious Website category is a broad cautionary result rather than an assertion that every short link or hosted object is harmful.
- Public artifact URL https://gridinsoft.com/online-virus-scanner/url/glacat-com
-
HTTP status
200 - Page element The fresh result contained no positive behavior signal.
- Analyst observation The fresh result did not name a concrete harmful glacat.com URL, destination, file, payload, receiver, command, exploit, or hash.
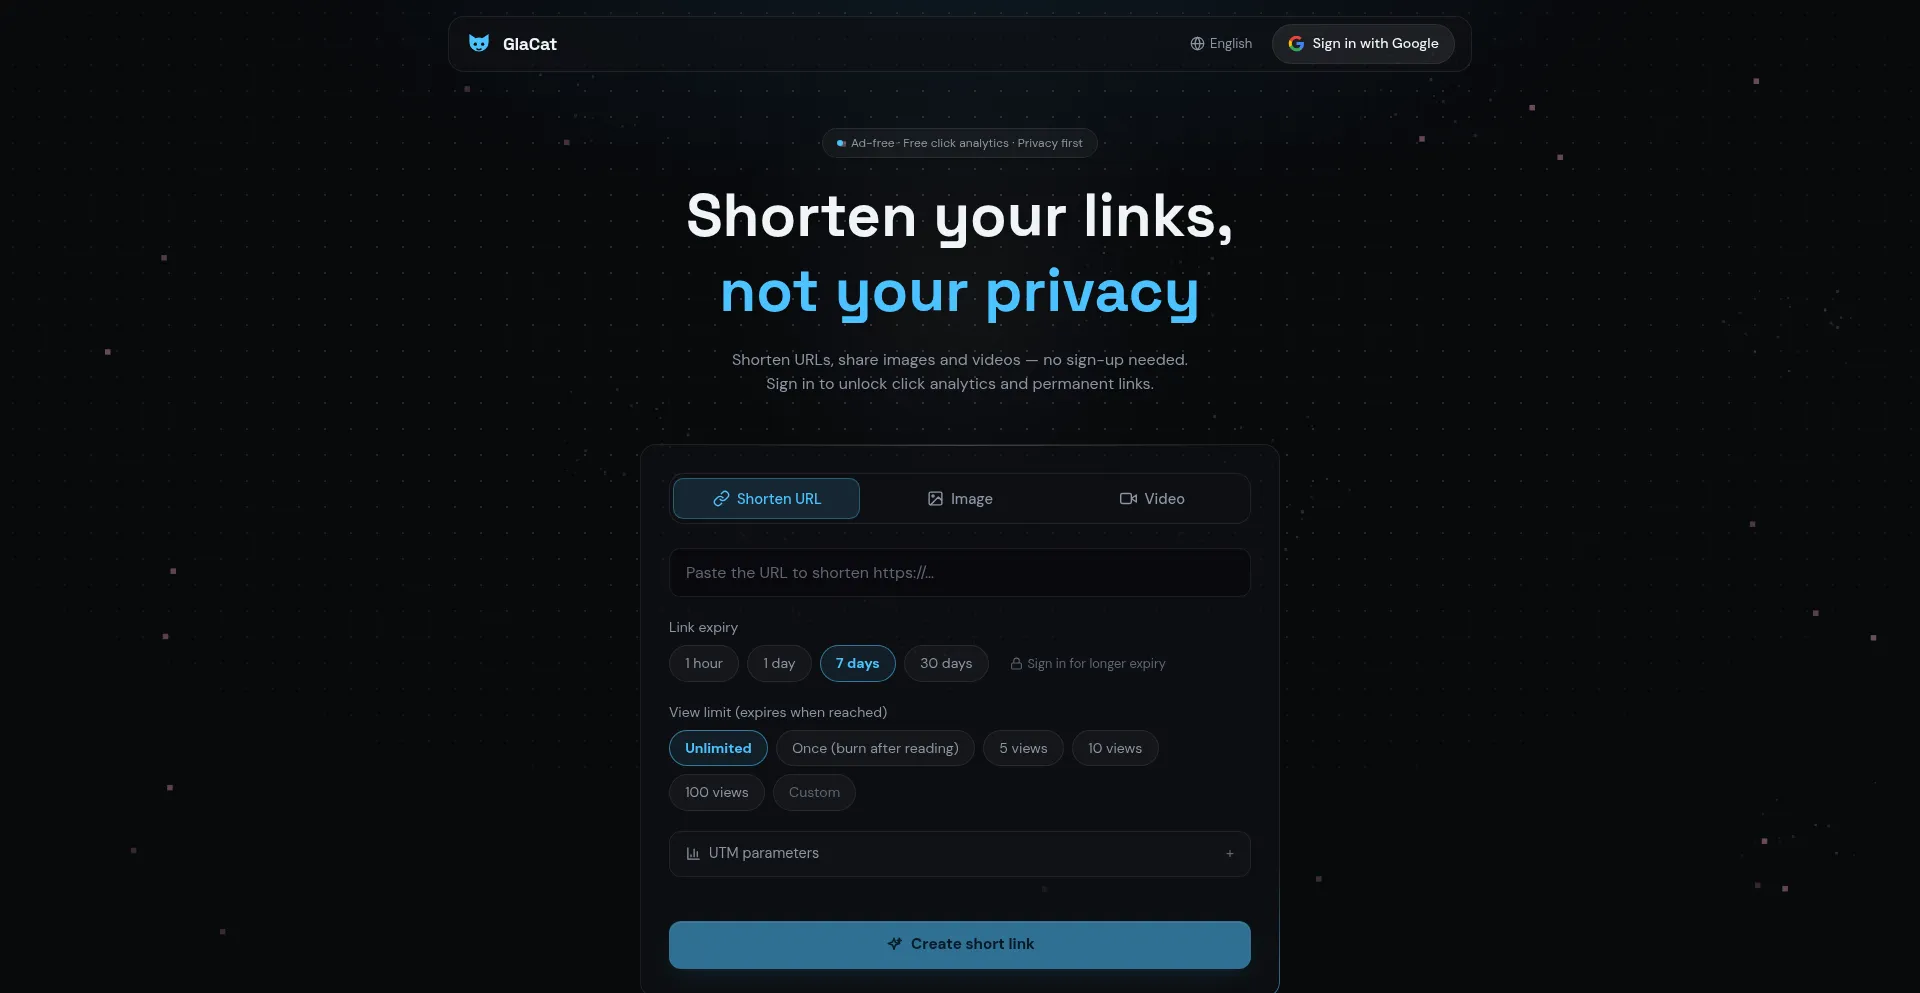
The apex and the public security, no-ads, burn, share, about, privacy, and terms pages returned HTTP 200 and consistently presented GlaCat as a user-controlled URL-shortening and file-, image-, and video-sharing service. The reviewed root and public pages did not redirect to an unrelated host, request non-provider credentials, initiate an executable or archive download, or expose a malware payload. The service states that it checks new URLs, rate-limits creation, uses Turnstile for anonymous requests, and accepts abuse reports; these are operator claims and visible controls, not independent proof that every user object is screened successfully.
-
HTTP status
200 - Page element The public interface offers URL shortening and file, image, and video sharing.
- Page element The security page describes URL checks, creation rate limits, Turnstile, and an abuse-report address.
- Analyst observation No unrelated redirect, non-provider credential request, executable or archive download, or malware payload was observed on the reviewed root and public information pages.
Twenty-eight distinct exact short codes surfaced by public URL intelligence, historical captures, or exact search were checked directly with desktop, mobile, crawler, and Gridinsoft-review request profiles. Every checked code currently returned the same GlaCat HTTP 404 response without a Location header. None currently exposed a redirect, credential receiver, downloadable file, malware payload, or hash. This supports removal or expiry of the known public objects, but it does not enumerate all current private or unindexed codes and files.
-
HTTP status
404 - Analyst observation All 28 known codes returned HTTP 404 without a Location header across five request profiles.
- Analyst observation Checked codes: /uGB03mp, /uJzoyJ3, /uL39GYn, /u2X8WA2, /uvfJCpg, /usyZb2i, /uE1z7vD, /u8tpyYn, /uE22eyb, /uMSx1nw, /uI3qoMN, /uBBwrod, /uFtOVeI, /unIgFpC, /ufmkyoE, /uCoW7sC, /uymMmVo, /uxAXjBn, /uDLa5I1, /uOClpWB, /uSzCJEJ, /u3WDt8h, /ubNU3fL, /uGC3Kcu, /uZcXIvH, /uSrlY37, /ukhx9LJ, and /uCvBJmF.
- Analyst observation A synthetic nonexistent code also returned the same HTTP 404 response and no redirect.
Public urlscan captures from 2026 preserved exact GlaCat short codes returning HTTP 302 to unrelated hosts and payment- or brand-like paths. Representative destinations included mdmh-pinebluff.com, rngtechindia.com, eurobank.s-host.net, eopyy.s-host.net, bingo-cafe.com, bingo-kaffee.com, bingo-coffee.com, and crowhurst.com.au. The preserved destination pages available during this review showed a hosting bot-block page or HTTP 404 rather than a captured credential form or malware delivery. These records are reproducible evidence of historical redirect abuse at the exact-object level, but they do not establish a specific phishing payload, credential receiver, malware file, or hash, and the corresponding GlaCat codes now return HTTP 404.
- Public artifact URL https://urlscan.io/result/019d6d43-f5b0-73cc-81d6-5500caed9423/
-
Redirect destination
https://mdmh-pinebluff.com/r/50ooO3O7 -
Redirect destination
https://rngtechindia.com/pay/pLF9LD52 -
Redirect destination
https://eurobank.s-host.net/KQxXmItm -
Redirect destination
https://eopyy.s-host.net/pay/BjQ21x6L -
Redirect destination
https://bingo-cafe.com/QOQpz2xb - Analyst observation The preserved scans demonstrate historical exact short-link redirects to unrelated hosts, while the available final-page captures showed a bot block or HTTP 404 and did not expose a credential receiver, malware payload, file, or hash.
The exact submitted host and registrable parent are the same glacat.com apex. urlscan reported 2,741 public scans and supplied historical exact-object redirect evidence; recent results concentrated on a small set of now-disabled codes and did not carry a malicious urlscan verdict. OTX retained sixteen PhishDestroy-related pulse associations and ten URL observations for the apex, while www.glacat.com had no DNS answer. Current public URLhaus, OpenPhish, Phishing.Database, ThreatFox, and PhishDestroy active-feed snapshots contained no exact glacat.com match.
- Public artifact URL https://urlscan.io/domain/glacat.com
- Public artifact URL https://otx.alienvault.com/indicator/domain/glacat.com
- Public artifact URL https://web.archive.org/web/*/glacat.com/*
- Analyst observation urlscan reported 2,741 public scans; OTX retained 16 PhishDestroy-related pulse associations and 10 URL observations.
- Analyst observation The current public URLhaus, OpenPhish, Phishing.Database, ThreatFox, and PhishDestroy active-feed snapshots contained no exact glacat.com match.
- Analyst observation Exact-host and parent-domain OSINT refer to the same glacat.com apex; www.glacat.com did not resolve.
Wayback returned 114 collapsed records for the apex and 218 wildcard records. A 2021 root snapshot belonged to an earlier parked-domain lifecycle, while snapshots from 2024 onward presented the GlaCat service. One archived exact code from 2024 returned a structured not-found response rather than a redirect. The archive did not preserve an exact credential form, malware file, payload, or hash on the apex, but archive coverage is finite and does not enumerate private, deleted, or unrecorded short links and hosted files.
- Public artifact URL https://web.archive.org/web/*/glacat.com/*
- Analyst observation Wayback returned 114 collapsed apex records and 218 wildcard records.
- Analyst observation The 2021 root was parked under an earlier lifecycle; snapshots from 2024 onward presented the GlaCat service.
- Analyst observation The archived exact path /uBBwrod returned a structured not-found response with no redirect destination.
The current external snapshot retained thirteen malicious and one suspicious results. The adverse engines used domain-level blacklist methods and applied phishing, malware, malicious, or suspicious labels; separate providers also retained Avira, Norton, and Bitdefender warnings. The available entries did not identify the exact active URL, response, credential receiver, file, payload, or hash that produced the label. They document current reputation disagreement and historical abuse context, not a reproducible current harmful object.
- Page element External snapshot: 13 malicious and 1 suspicious domain-level results.
- Analyst observation The adverse engines used blacklist methods and did not name an exact currently active glacat.com URL, response, file, payload, receiver, or hash.
- Analyst observation Domain-level blacklist categories are distinct from a captured exact URL with observable harmful behavior.
glacat.com is a public user-controlled short-link and file-sharing namespace. The root provides creation interfaces but no complete directory of active, private, deleted, or future short codes and files. Twenty-eight public exact codes were found and reviewed, yet the material namespace cannot be independently enumerated. A clean current finite sample and stated abuse controls therefore cannot support a domain-wide Safe certification. Future harmful-content claims and remediation decisions should identify and review the exact short URL or hosted object and its user-visible destination or content.
- Page element The root exposes public URL-shortening and file-sharing creation interfaces but no complete object directory.
- Analyst observation Twenty-eight known public codes were reviewed, but the complete current, private, deleted, and future namespace was not publicly enumerable.
- Analyst observation A domain-wide Safe verdict cannot be inferred from a clean root or a finite set of disabled user-controlled objects.
Scope and limitations
- The exact submitted host is the registrable parent domain, so exact-host and parent-domain OSINT refer to the same glacat.com apex; the nonexistent www alias was checked separately.
- The review covered the fresh Gridinsoft result, the root and seven public information pages, twenty-eight exact public short codes, multiple desktop, mobile, crawler, and review profiles, DNS, TLS, public URL intelligence, threat-intelligence context, active phishing and malware feeds, historical captures, and archive records.
- The complete current, private, unindexed, deleted, and future short-code and hosted-file namespace is not publicly enumerable. Twenty-eight known public objects were reviewed, but no statement is made about unobserved objects.
- Historical urlscan records preserved redirects to unrelated hosts, but the available final-page captures showed a bot block or HTTP 404. The review therefore does not claim that a particular credential receiver, malware file, payload, or hash was captured.
- The service's security, rate-limit, Turnstile, and abuse-report statements were observed as operator claims and visible controls; their effectiveness for every user-created object was not independently verified.
- Conditional, geographic, account-bound, language-dependent, referrer-dependent, device-dependent, or time-limited content could differ outside the reviewed request profiles and locations.
- Public search, urlscan, OTX, archive, feed, and sandbox indexes are finite. Absence from current active feeds does not prove that no unindexed or historical harmful object existed.
- Historical threat-intelligence and certificate records are incomplete; gaps in that coverage do not establish safety.
- External blacklist and threat-intelligence labels remain independently controlled context. They are not equivalent to a current reproducible malicious URL or sample and did not determine the Gridinsoft verdict.
- The verdict does not certify every current or future short link or hosted file as safe and is not a guarantee against later content or destination changes.


Help protect others by sharing this page on social media! The more people who know about glacat.com, the fewer chances they have to deceive someone else. Help others evaluate glacat.com by sharing this page on social media!